

THREAT REMOVAL

Remove 11.lv Casino Ads
11.lv pop-up ads can affect your browser. 11.lv is a domain that will show pop-up ads and may redirect you if you click on any of the said ads. 11.lv is a malicious URL address used for the purposes of…
11.lv pop-up ads can affect your browser. 11.lv is a domain that will show pop-up ads and may redirect you if you click on any of the said ads. 11.lv is a malicious URL address used for the purposes of…

Woxx.xyz redirect can affect your browser. Woxx.xyz is a redirect, that will get in your browser. Woxx.xyz can push redirects and ads. Woxx.xyz is connected to a few malicious domains with redirecting URLs of websites containing spam, advertisements or even…

Cudalbapt.com push notifications can affect your browser. Cudalbapt.com will display ads, pop-ups and messages wanting you to allow permissions for a page on the Web. Cudalbapt.com is a malicious URL address used for the purposes of redirecting users and showing…

Opgolan.com redirect can affect your browser. Opgolan.com is a redirect, that will get in your browser. Opgolan.com can push redirects and ads. Opgolan.com is a malicious domain connected with redirecting URLs of websites containing spam, advertisements or even some sort…

Heplopetithe.pro is a suspicious website that displays pop-up window and attempts to receive permission to generate push notifications with sponsored content. To make you more prone to agree to receive sponsored content in the browser and even on the desktop,…
The .Artemis865-20 virus is a ransomware that is currently set against target end users on a global scale. There is no information available about the hacking group behind it. It is believed to be a new iteration of the famous…

Tinhanandhatar.info is a browser redirect that may be pushed by potentially unwanted program or triggered by a script injected in another bogus website. Its purpose is to trick you into subscribing to push notifications so that it can start delivering…
Ransomware continues to be a top threat to both individuals and enterprises. And protection against it is more important than ever. So, it is definitely good news that Cameyo, an application virtualization software-as-a-service platform, is launching a new RDP Port…

Samepinstar.com redirect can affect your browser. Samepinstar.com is a redirect, that will get in your browser. Samepinstar.com can push redirects and ads. Samepinstar.com is a malicious domain connected with redirecting URLs of websites containing spam, advertisements or even some sort…

Carbamylife.info pop-up ads can affect your browser. Carbamylife.info is a domain that will show pop-up ads and may redirect you if you click on any ads. Carbamylife.info is a malicious URL address used for the purposes of redirecting users via…

Folmetor.com push notifications can affect your browser. Folmetor.com will display ads, pop-ups and messages wanting you to allow permissions for a page on the Web. Folmetor.com is a malicious URL address used for the purposes of redirecting users and showing…

Win Magician is a software promoted as a system optimization tool. However, it is also categorized as a potentially unwanted program due to the shady mechanisms used for its spread across the web. Oftentimes, it lands on computer systems without…
To our greatest concern, the services we use daily often become part of data breaches and data leaks, in which our personal details are exposed to cybercriminals. Banks, airlines, hotels, various organizations put our information at risk in databases that…

What is the Mac.advancesystemcare.co virus on Mac? How to remove Mac.advancesystemcare.co from Mac? How to stop WARNING redirect pages fully? Mac.advancesystemcare.co is the name of a web page that appears on users’ Macs as a result of a potentially unwanted…

Appi.space push notifications can affect your browser. Appi.space will display ads, pop-ups and messages wanting you to allow permissions for a page on the Web. Appi.space is a malicious URL address used for the purposes of redirecting users and showing…
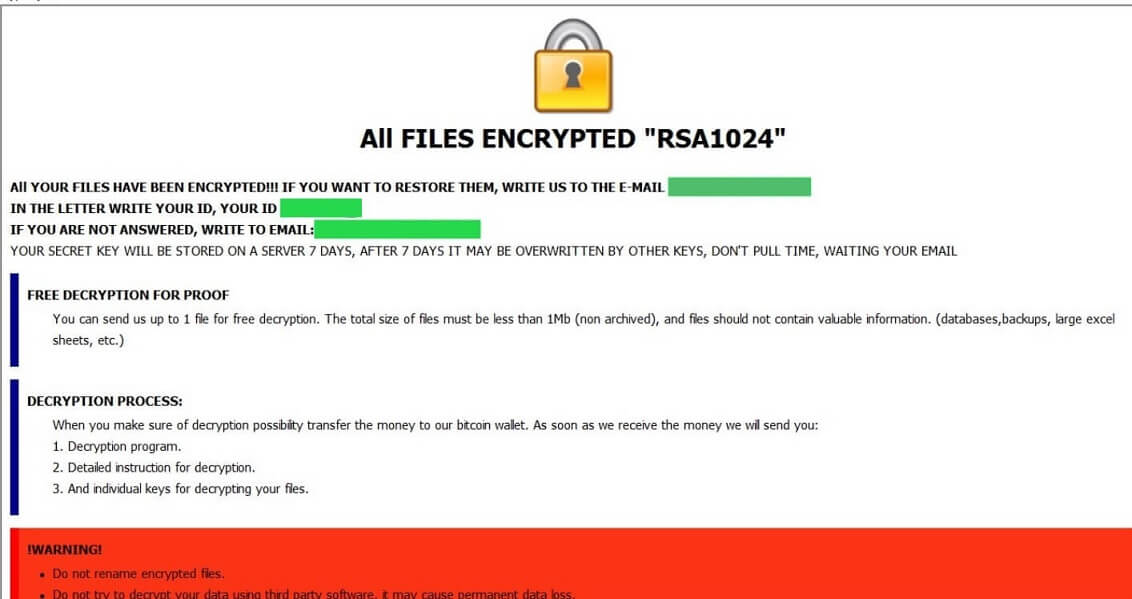
.money file virus is also known as Dharma ransomware which encrypts files and demands a ransom. .money file virus uses cmdroot@airmail.cc as a contact. Dharma ransomware is back with a new cryptovirus variant. The current version of the Dharma family…
Does your computer seem to be running slower than usual, or are you noticing an uptick in unwanted ads and pop-ups? Chances are, you might have SlimCleaner Plus installed on your system. Marketed as a tool to boost your PC’s…
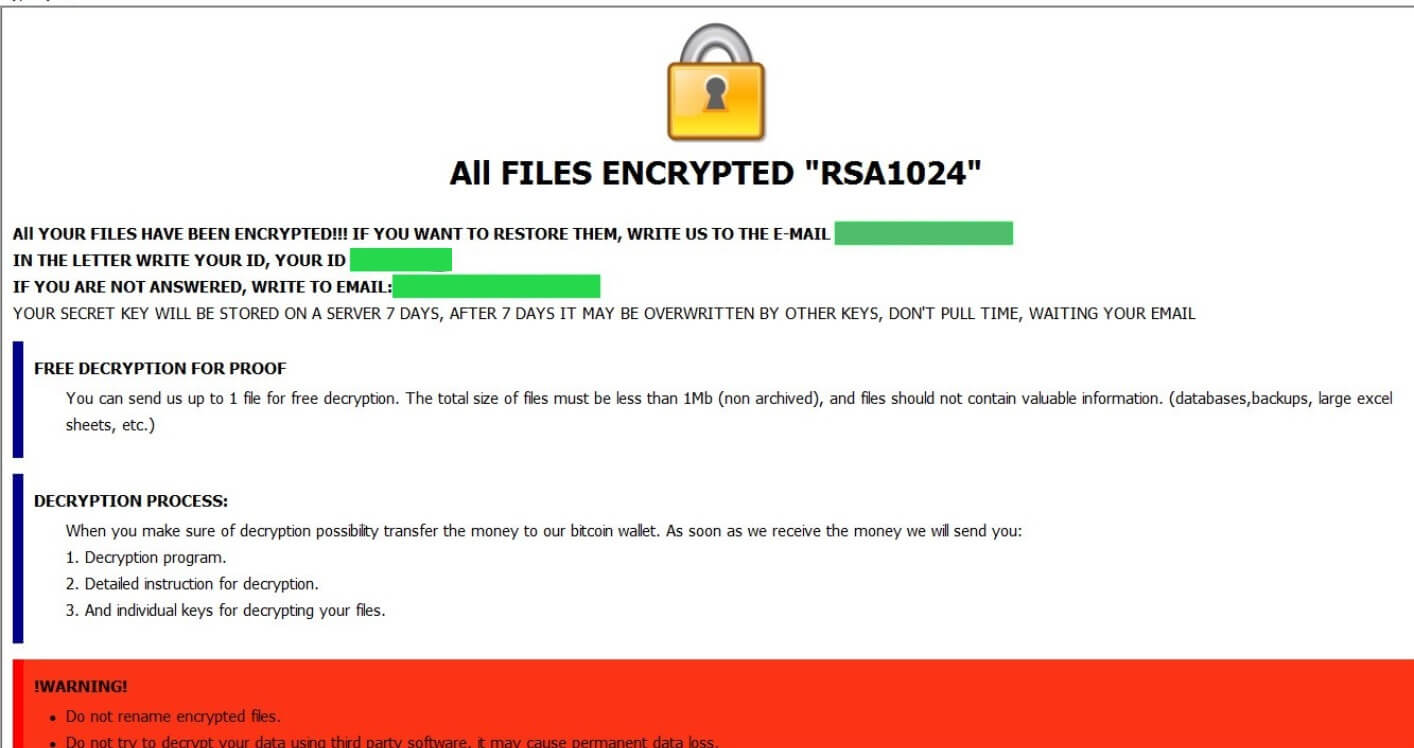
What is .RSA file virus? The virus is also known as Dharma ransomware which encrypts files. .RSA file virus uses rsa1024@tutanota.com as a contact. Dharma ransomware is back with a new cryptovirus variant. The current version of the Dharma family…

The domain Mirox23.biz is used for the spread of annoying online ads. It tends to load in frequently used web browsers without users’ permission. Once the browser loads Mirox23.biz, the website generates a pop-up window appears that urges users to…
Small to mid-sized businesses (SMBs) are more targeted by cybercriminals than ever, according to a new AlertLogic report. However, there is a way for SMBs to be protected and it involves cushioning the ports that cyber attackers target the most.…