

A Trojan:Win32/Kepavll!rfn detection from Windows Defender or another security product is not a notification to dismiss or ignore. This detection name represents a heuristic identification of a trojan-category threat – software engineered to operate covertly on your system while performing actions that benefit its operators at your expense. Acting quickly when this alert appears is critical to limiting potential damage, which may include data theft, account compromise, or further malware installation.
Trojan:Win32/Kepavll!rfn is a detection name used by Microsoft Defender Antivirus to identify a trojan threat in the Win32 (Windows) environment. The “!rfn” suffix indicates a heuristic or generic detection pattern rather than a signature matched to one specific file, meaning Defender has identified behavioral or structural characteristics consistent with known trojan families. As documented in Microsoft Security Intelligence, trojans in this category may perform a range of malicious activities including remote access, data harvesting, credential theft, or serving as a loader that delivers additional malware onto the system.
| Name | Trojan:Win32/Kepavll!rfn |
| Threat Type | Trojan (Microsoft Defender Heuristic Detection) |
| Symptoms | Microsoft Defender alert for Trojan:Win32/Kepavll!rfn; suspicious processes running in Task Manager; unexpected network activity; sluggish system performance; potential credential theft behavior; browser anomalies or unauthorized account access |
| Removal Time | Around 15 Minutes |
| Removal Tool | See If Your System Has Been Affected by Malware
* Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. SpyHunter’s EULA, Privacy Policy, and more details about Free Remover. |
How Did I Get Trojan:Win32/Kepavll!rfn?
Security researchers document the following as the primary distribution channels for trojan threats of this type:
- Cracked software, key generators, and game cheats downloaded from unofficial sources, torrent sites, and warez platforms – this is the single most common delivery method for Win32 trojans.
- Malicious email attachments – particularly Microsoft Office documents with embedded macros that execute the trojan payload when the user enables macro content.
- Drive-by download attacks – automatic downloads triggered when visiting compromised websites that exploit unpatched vulnerabilities in browsers or browser plugins.
- Fake software update prompts displayed by malicious websites claiming that Java, Flash, or another common component requires an urgent update.
- Files shared through gaming communities – Discord servers, game modification forums, and file-sharing platforms where malicious files are distributed disguised as game content.
- Pirated media packages including movies, TV series, or software that contain trojan payloads bundled with the content.
What Does Trojan:Win32/Kepavll!rfn Do?
Trojans flagged by Microsoft Defender under the Kepavll detection family are associated with the following capabilities based on documented behavior patterns:
- Establishes persistence on the infected system through Windows registry modifications, scheduled tasks, or placement in startup folders to survive system reboots.
- Connects to remote command-and-control servers to receive updated instructions, deliver stolen data, or download additional malware components.
- Keylogging capability – may record all keystrokes entered on the infected device, capturing passwords, credit card numbers, and other sensitive input.
- Browser credential harvesting – extracts saved passwords, autofill data, session cookies, and browsing history from installed browsers.
- Dropper functionality – may download and execute additional malware including ransomware, additional trojans, or coin mining software.
- Security software interference – may attempt to disable or exclude itself from Windows Defender or other installed security products.
- Potential remote access capability – some variants grant attackers the ability to remotely control the infected machine, browse files, or execute commands.
- Data exfiltration – collected credentials and system information are transmitted to attacker-controlled infrastructure.
How to Remove Trojan:Win32/Kepavll!rfn?
Given the data theft potential of this threat, speed and thoroughness are equally important in the removal process:
- Disconnect from the internet immediately to stop any ongoing data exfiltration to attacker servers while you prepare for removal.
- Boot into Safe Mode with Networking – restart, hold Shift and click Restart, then navigate to Troubleshoot – Advanced Options – Startup Settings – press 5. Safe Mode prevents most trojans from loading at startup.
- Run a full system scan with SpyHunter in Safe Mode to identify and quarantine all components associated with the trojan.
- Allow Microsoft Defender to complete its removal action if it has already quarantined the file – accept the recommended action in the Defender notification or Virus and Threat Protection panel.
- Open Task Manager and end any suspicious or unfamiliar processes – research any process names you do not immediately recognize before ending them.
- Review installed programs in Settings – Apps and remove any applications you do not recognize, particularly those installed around the time the detection first appeared.
- Check Task Scheduler and MSConfig startup entries for persistence mechanisms added by the trojan and delete or disable any suspicious entries found.
- Inspect registry Run keys (regedit – HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRun and the HKEY_LOCAL_MACHINE equivalent) and remove any entries pointing to unfamiliar file paths.
- Change all account passwords immediately after removal – email, banking, social media, and gaming accounts – using a separate clean device. Assume any credentials entered on this machine since the infection may have been captured.
- Monitor accounts for unauthorized activity in the weeks following the infection and enable two-factor authentication on all important accounts.

Ventsislav Krastev
Ventsislav is a cybersecurity expert at SensorsTechForum since 2015. He has been researching, covering, helping victims with the latest malware infections plus testing and reviewing software and the newest tech developments. Having graduated Marketing as well, Ventsislav also has passion for learning new shifts and innovations in cybersecurity that become game changers. After studying Value Chain Management, Network Administration and Computer Administration of System Applications, he found his true calling within the cybersecrurity industry and is a strong believer in the education of every user towards online safety and security.
Follow Me:
Preparation before removing Trojan:Win32/Kepavll!rfn.
Before starting the actual removal process, we recommend that you do the following preparation steps.
- Make sure you have these instructions always open and in front of your eyes.
- Do a backup of all of your files, even if they could be damaged. You should back up your data with a cloud backup solution and insure your files against any type of loss, even from the most severe threats.
- Be patient as this could take a while.
- Scan for Malware
- Fix Registries
- Remove Virus Files
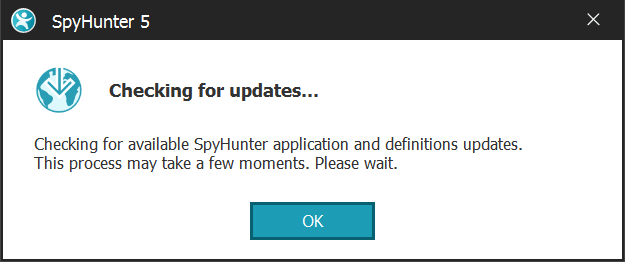
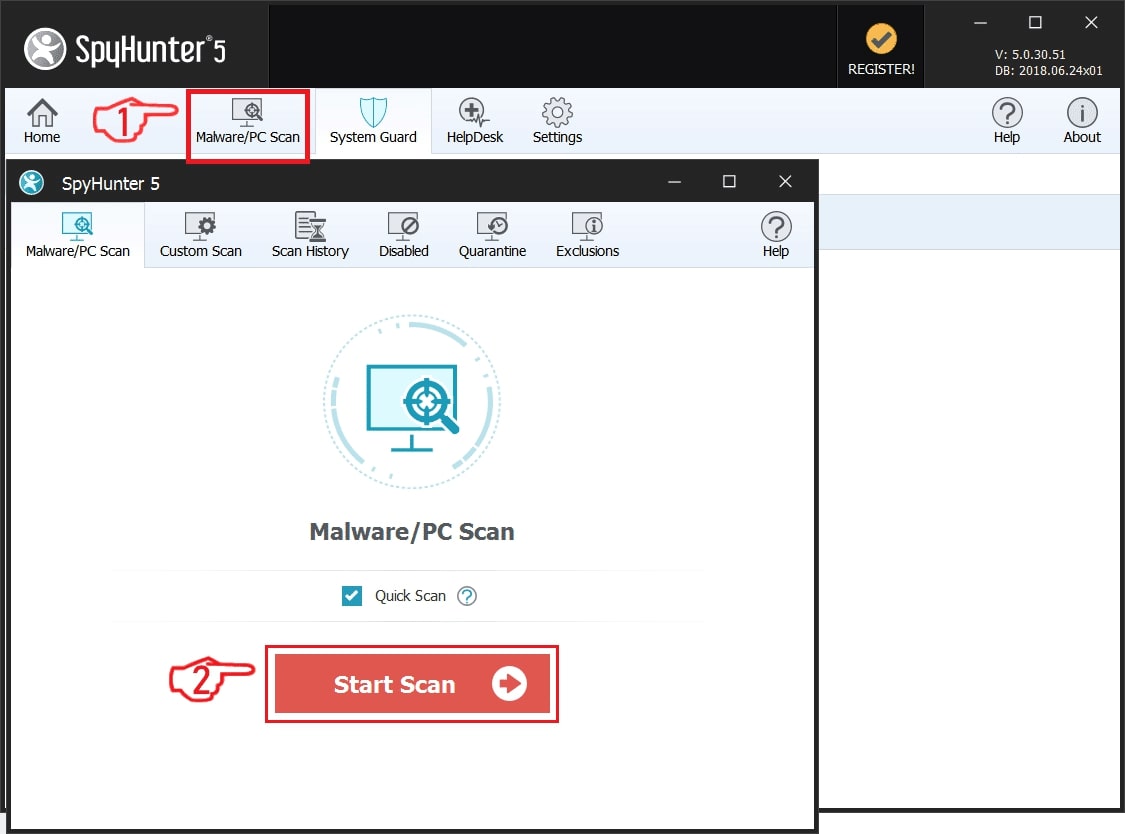
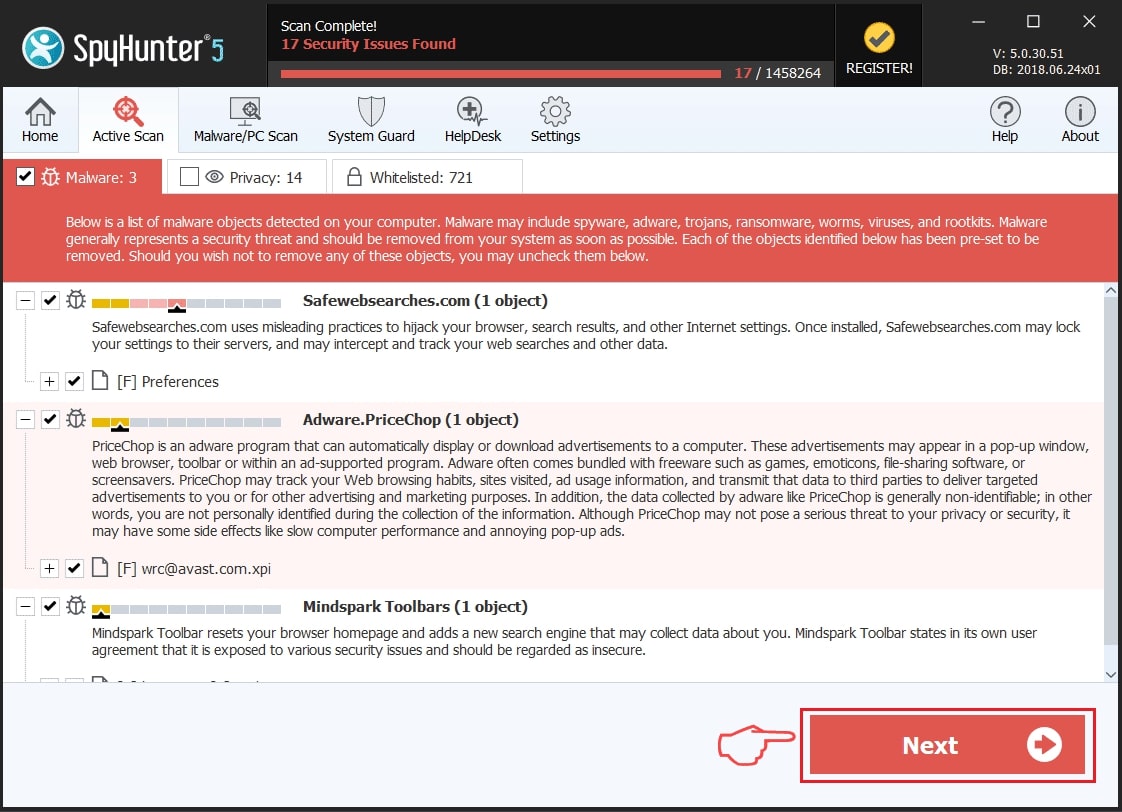
Step 1: Scan for Trojan:Win32/Kepavll!rfn with SpyHunter Anti-Malware Tool
Step 2: Clean any registries, created by Trojan:Win32/Kepavll!rfn on your computer.
The usually targeted registries of Windows machines are the following:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
You can access them by opening the Windows registry editor and deleting any values, created by Trojan:Win32/Kepavll!rfn there. This can happen by following the steps underneath:
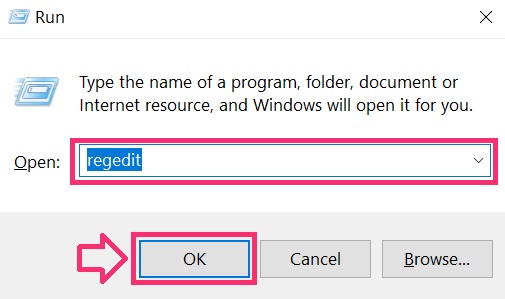
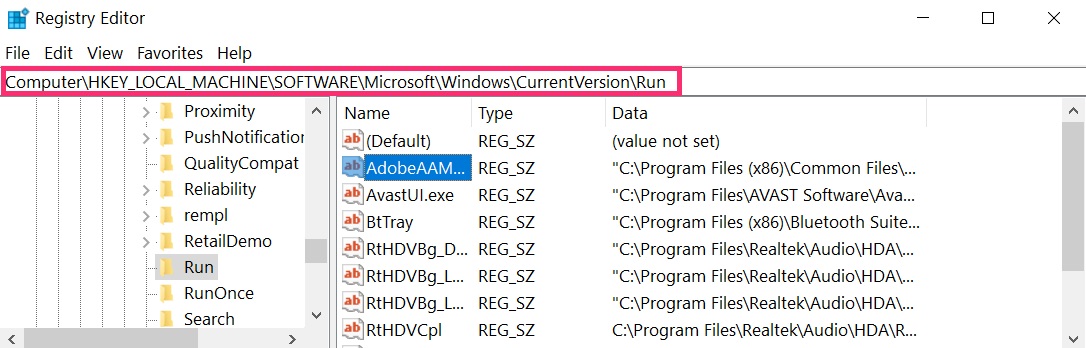
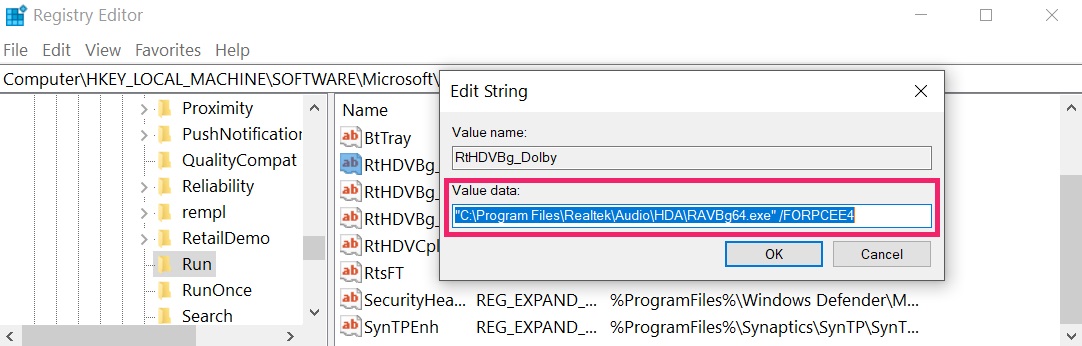 Tip: To find a virus-created value, you can right-click on it and click "Modify" to see which file it is set to run. If this is the virus file location, remove the value.
Step 3: Find virus files created by Trojan:Win32/Kepavll!rfn on your PC.
1.For Windows 8, 8.1 and 10.
For Newer Windows Operating Systems
1: On your keyboard press + R and write explorer.exe in the Run text box and then click on the Ok button.
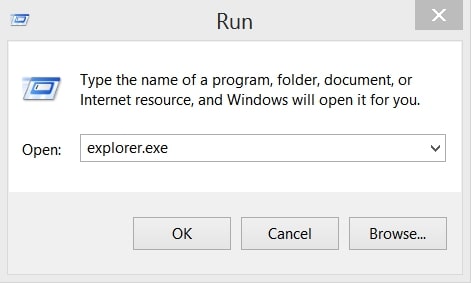
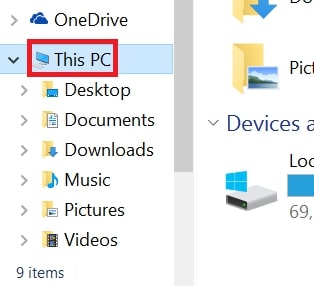
2: Click on your PC from the quick access bar. This is usually an icon with a monitor and its name is either “My Computer”, “My PC” or “This PC” or whatever you have named it.
3: Navigate to the search box in the top-right of your PC's screen and type “fileextension:” and after which type the file extension. If you are looking for malicious executables, an example may be "fileextension:exe". After doing that, leave a space and type the file name you believe the malware has created. Here is how it may appear if your file has been found:
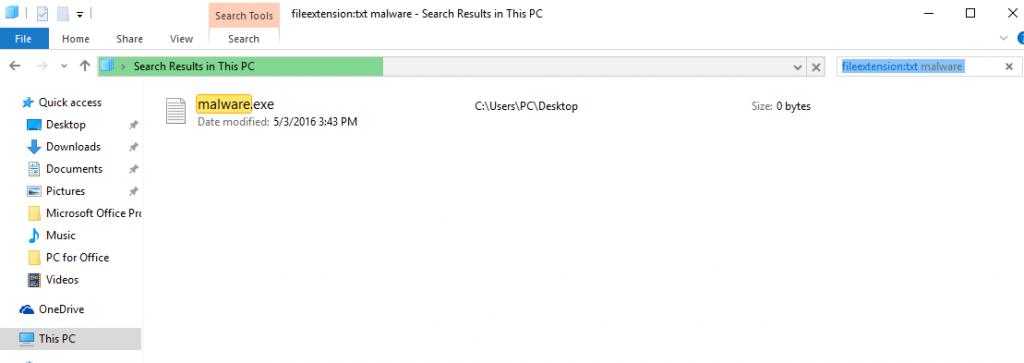
N.B. We recommend to wait for the green loading bar in the navigation box to fill up in case the PC is looking for the file and hasn't found it yet.
2.For Windows XP, Vista, and 7.
For Older Windows Operating Systems
In older Windows OS's the conventional approach should be the effective one:
1: Click on the Start Menu icon (usually on your bottom-left) and then choose the Search preference.
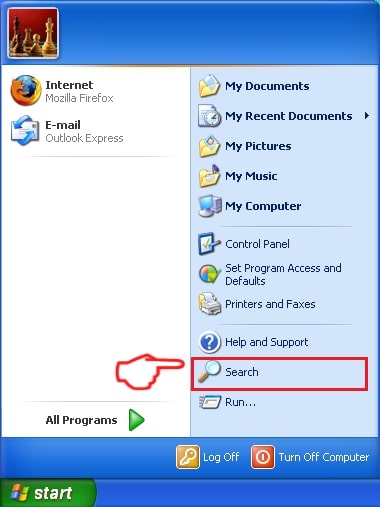
2: After the search window appears, choose More Advanced Options from the search assistant box. Another way is by clicking on All Files and Folders.
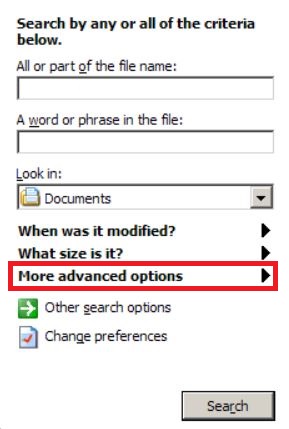
3: After that type the name of the file you are looking for and click on the Search button. This might take some time after which results will appear. If you have found the malicious file, you may copy or open its location by right-clicking on it.
Now you should be able to discover any file on Windows as long as it is on your hard drive and is not concealed via special software.
Trojan:Win32/Kepavll!rfn FAQ
What Does Trojan:Win32/Kepavll!rfn Trojan Do?
The Trojan:Win32/Kepavll!rfn Trojan is a malicious computer program designed to disrupt, damage, or gain unauthorized access to a computer system. It can be used to steal sensitive data, gain control over a system, or launch other malicious activities.
Can Trojans Steal Passwords?
Yes, Trojans, like Trojan:Win32/Kepavll!rfn, can steal passwords. These malicious programs are designed to gain access to a user's computer, spy on victims and steal sensitive information such as banking details and passwords.
Can Trojan:Win32/Kepavll!rfn Trojan Hide Itself?
Yes, it can. A Trojan can use various techniques to mask itself, including rootkits, encryption, and obfuscation, to hide from security scanners and evade detection.
Can a Trojan be Removed by Factory Reset?
Yes, a Trojan can be removed by factory resetting your device. This is because it will restore the device to its original state, eliminating any malicious software that may have been installed. Bear in mind that there are more sophisticated Trojans that leave backdoors and reinfect even after a factory reset.
Can Trojan:Win32/Kepavll!rfn Trojan Infect WiFi?
Yes, it is possible for a Trojan to infect WiFi networks. When a user connects to the infected network, the Trojan can spread to other connected devices and can access sensitive information on the network.
Can Trojans Be Deleted?
Yes, Trojans can be deleted. This is typically done by running a powerful anti-virus or anti-malware program that is designed to detect and remove malicious files. In some cases, manual deletion of the Trojan may also be necessary.
Can Trojans Steal Files?
Yes, Trojans can steal files if they are installed on a computer. This is done by allowing the malware author or user to gain access to the computer and then steal the files stored on it.
Which Anti-Malware Can Remove Trojans?
Anti-malware programs such as SpyHunter are capable of scanning for and removing Trojans from your computer. It is important to keep your anti-malware up to date and regularly scan your system for any malicious software.
Can Trojans Infect USB?
Yes, Trojans can infect USB devices. USB Trojans typically spread through malicious files downloaded from the internet or shared via email, allowing the hacker to gain access to a user's confidential data.
About the Trojan:Win32/Kepavll!rfn Research
The content we publish on SensorsTechForum.com, this Trojan:Win32/Kepavll!rfn how-to removal guide included, is the outcome of extensive research, hard work and our team’s devotion to help you remove the specific trojan problem.
How did we conduct the research on Trojan:Win32/Kepavll!rfn?
Please note that our research is based on an independent investigation. We are in contact with independent security researchers, thanks to which we receive daily updates on the latest malware definitions, including the various types of trojans (backdoor, downloader, infostealer, ransom, etc.)
Furthermore, the research behind the Trojan:Win32/Kepavll!rfn threat is backed with VirusTotal.
To better understand the threat posed by trojans, please refer to the following articles which provide knowledgeable details.