

What is Trojan:Win32/Ravartar!rfn?
Microsoft Defender flagged Trojan:Win32/Ravartar!rfn and the alert keeps returning, or you want to understand whether this detection is real or a false positive and exactly what to do about it. Read this guide carefully before taking any action in Defender.
Trojan:Win32/Ravartar!rfn is a Microsoft Defender detection and Microsoft Security Intelligence. The !rfn suffix confirms it is reputation and behavior-based rather than an exact signature match. Microsoft states the threat can perform actions chosen by a malicious actor, and that technical details are not publicly available. Gridinsoft verdict: a Ravartar alert from a crack, installer, archive, script, fake update, or email attachment should be treated as real malware until proven otherwise. Users on Microsoft Q&A forums report the threat keeps returning, with FRST logs confirming persistence components that standard scans alone do not address.
Trojan:Win32/Ravartar!rfn Short Overview
| Type | Microsoft Defender !rfn (reputation/behavior-based) detection – threat can perform attacker-chosen actions; Microsoft has not published technical details; documented by Gridinsoft July 2026. |
| Symptoms | Defender flagging Trojan:Win32/Ravartar!rfn, the alert returning after quarantine, a detection pointing to a crack/Temp/AppData path or a PowerShell context, or the threat persisting across multiple scans. |
| Removal Time | Approximately 15 minutes for a full-system scan |
| Removal Tool | See If Your System Has Been Affected by malware
Download
Malware Removal Tool
|
How Did I Get Trojan:Win32/Ravartar!rfn?
- A cracked application, archive, or pirated software installer – Gridinsoft specifically names cracks, repacks, and unofficial installers as the highest-risk delivery path. If the detection points to a file in the same directory as a keygen or crack, treat it as confirmed malicious.
- A malicious email attachment or PowerShell script – A document, archive, or script from a spam or phishing email executes the Trojan dropper when opened. If the alert references a PowerShell context (amsi path), a malicious script triggered the detection – find the script, the scheduled task, or the Run registry entry that launched it.
- An Outlook attachment cache – Gridinsoft documents the alert sometimes appearing in an Outlook attachment cache for a file that was never opened. If the attachment was never executed, risk is lower – but update Defender and run a full scan before restoring anything.
- Software bundling with unofficial free downloads – A free program from a third-party site installs the Ravartar component as a bundled addition through software bundling.
What Does Trojan:Win32/Ravartar!rfn Do?
- Performs malicious actor-directed actions with no disclosed specific payload – Microsoft Security Intelligence states the threat can perform a number of actions of a malicious actor’s choice, with technical details not publicly available. The payload is attacker-configurable and may include credential theft, additional malware download, ad injection, or remote access depending on the specific sample.
- Hides behind a normal-looking app or process – the Trojan is designed to appear harmless, behaving similarly to Trojan:Win32/Suschil!rfn and ChatGPTStealer – threats that present as legitimate software while operating maliciously in the background.
- Establishes persistence causing the alert to keep returning – Community reports on Microsoft Q&A confirm the threat returns repeatedly after Defender quarantines it. A persistence mechanism – a scheduled task, a startup registry entry, or a service – relaunches the detected component after removal.
- Abuses PowerShell in some variants – When the Ravartar alert points to a PowerShell process context, a malicious script is the source. The fix requires finding and removing the script and its launch mechanism, not deleting PowerShell itself.
False positive check: A false positive is appropriate only when the flagged file has a trusted source, a verified digital signature, a normal installation path, clean follow-up scans, and no execution or persistence symptoms. If any of those conditions is missing, treat the detection as real.
How to Remove Trojan:Win32/Ravartar!rfn [Fix]
- Keep the item quarantined – Do not click Allow or Restore. Open Defender Protection History, open the Ravartar!rfn event, and copy the full affected file path.
- Assess the path – If it is in a crack directory, Temp, AppData, or an Outlook cache for an unopened attachment, treat it as real malware and proceed with cleanup.
- If the alert references a PowerShell context – Do not delete PowerShell itself. Open Task Scheduler (taskschd.msc) and look for any task running PowerShell with an obfuscated or Base64-encoded argument. Also check the registry startup keys under HKCU and HKLM and recently created scripts in Temp and AppData. Delete the malicious script and its launch mechanism.
- Run a Microsoft Defender Offline Scan – Go to Windows Security, then Virus and Threat Protection, then Scan Options, then Microsoft Defender Offline Scan. This catches persistence components that hide during normal Windows startup.
- Use LockHunter for locked files – If Defender cannot remove a file because it is in use, use LockHunter (free tool) to unlock and delete it without a restart loop.
- If the alert still returns after all of the above – Use the Farbar Recovery Scan Tool (FRST) to generate a system scan log and post it to the MalwareTips or Malwarebytes forums for community-assisted cleanup. Stubborn Ravartar variants documented on Microsoft Q&A require a customized FRST fix script.
- Run a dedicated anti-malware tool as a second opinion – Use SpyHunter or Malwarebytes to catch any additional components Defender did not fully address.
Follow the complete removal guide below this article for the full step-by-step process.

Ventsislav Krastev
Ventsislav is a cybersecurity expert at SensorsTechForum since 2015. He has been researching, covering, helping victims with the latest malware infections plus testing and reviewing software and the newest tech developments. Having graduated Marketing as well, Ventsislav also has passion for learning new shifts and innovations in cybersecurity that become game changers. After studying Value Chain Management, Network Administration and Computer Administration of System Applications, he found his true calling within the cybersecrurity industry and is a strong believer in the education of every user towards online safety and security.
Follow Me:
Preparation before removing Trojan:Win32/Ravartar!rfn.
Before starting the actual removal process, we recommend that you do the following preparation steps.
- Make sure you have these instructions always open and in front of your eyes.
- Do a backup of all of your files, even if they could be damaged. You should back up your data with a cloud backup solution and insure your files against any type of loss, even from the most severe threats.
- Be patient as this could take a while.
- Scan for Malware
- Fix Registries
- Remove Virus Files
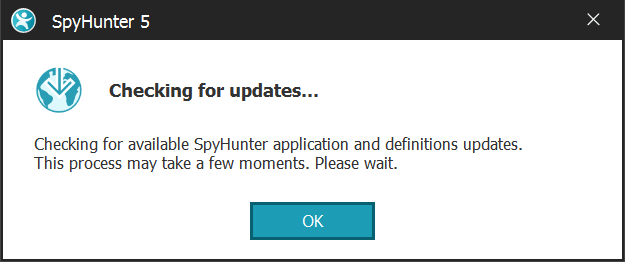
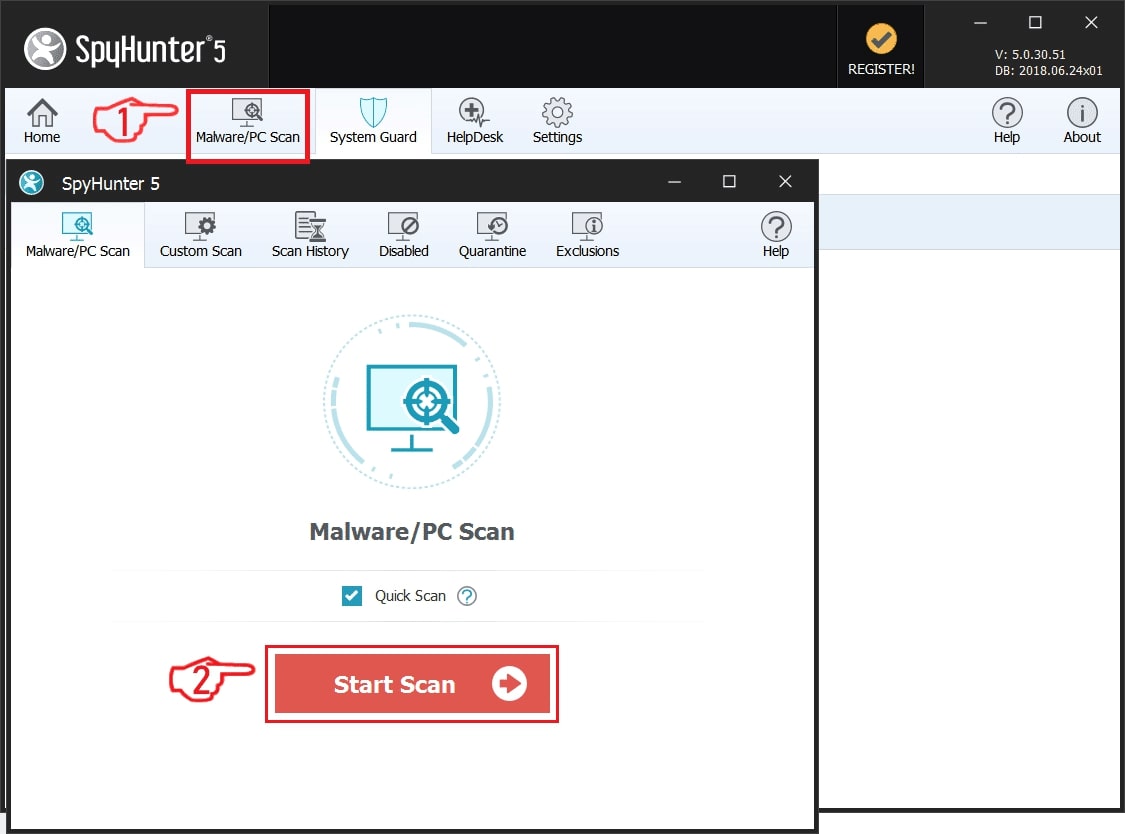
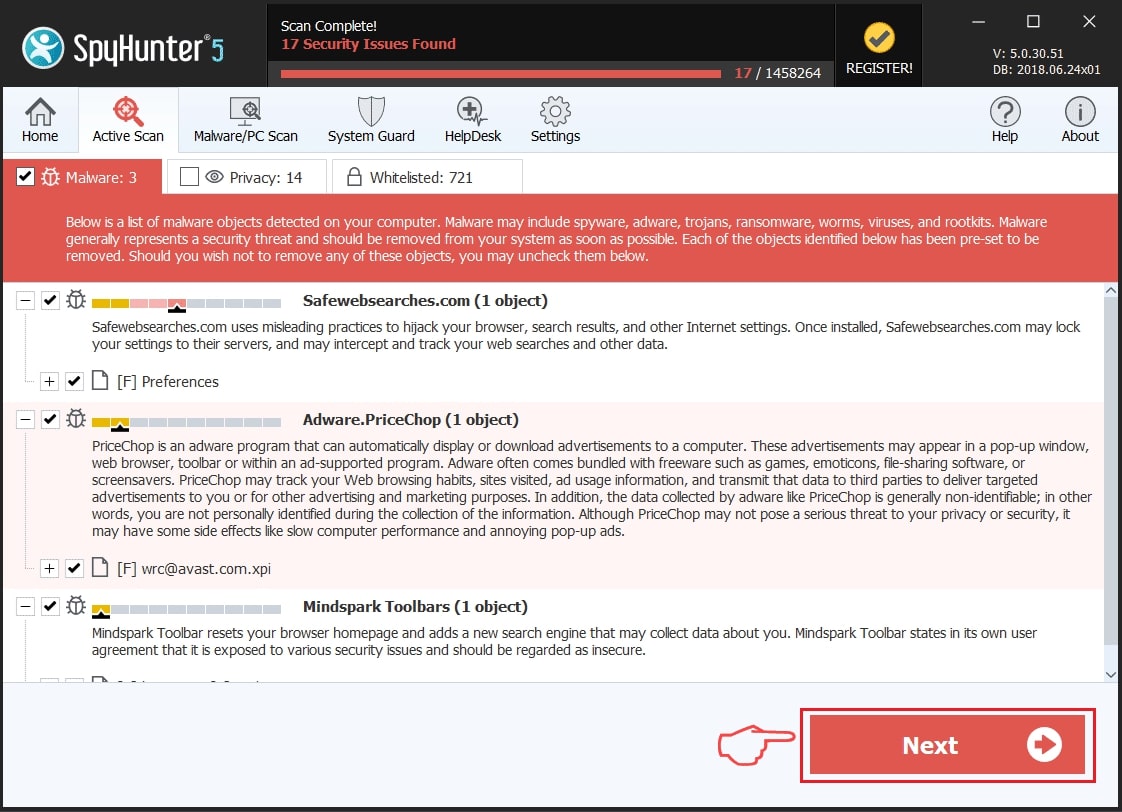
Step 1: Scan for Trojan:Win32/Ravartar!rfn with SpyHunter Anti-Malware Tool
Step 2: Clean any registries, created by Trojan:Win32/Ravartar!rfn on your computer.
The usually targeted registries of Windows machines are the following:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
You can access them by opening the Windows registry editor and deleting any values, created by Trojan:Win32/Ravartar!rfn there. This can happen by following the steps underneath:


 Tip: To find a virus-created value, you can right-click on it and click "Modify" to see which file it is set to run. If this is the virus file location, remove the value.
Step 3: Find virus files created by Trojan:Win32/Ravartar!rfn on your PC.
1.For Windows 8, 8.1 and 10.
For Newer Windows Operating Systems
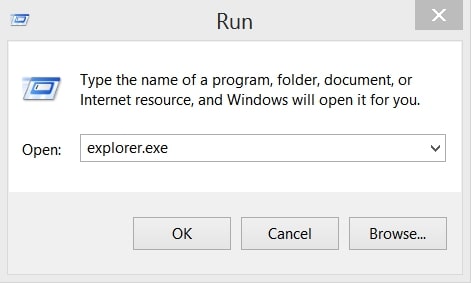
1: On your keyboard press + R and write explorer.exe in the Run text box and then click on the Ok button.
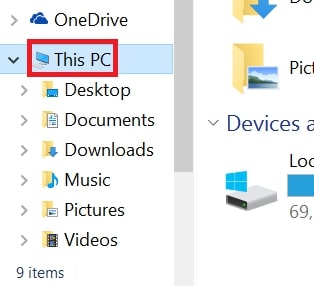
2: Click on your PC from the quick access bar. This is usually an icon with a monitor and its name is either “My Computer”, “My PC” or “This PC” or whatever you have named it.
3: Navigate to the search box in the top-right of your PC's screen and type “fileextension:” and after which type the file extension. If you are looking for malicious executables, an example may be "fileextension:exe". After doing that, leave a space and type the file name you believe the malware has created. Here is how it may appear if your file has been found:
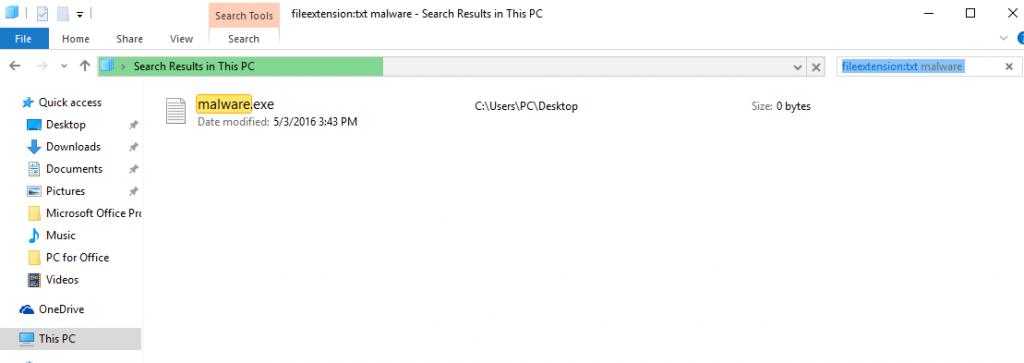
N.B. We recommend to wait for the green loading bar in the navigation box to fill up in case the PC is looking for the file and hasn't found it yet.
2.For Windows XP, Vista, and 7.
For Older Windows Operating Systems
In older Windows OS's the conventional approach should be the effective one:
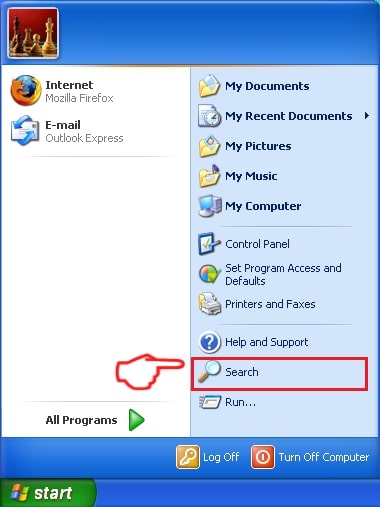
1: Click on the Start Menu icon (usually on your bottom-left) and then choose the Search preference.
2: After the search window appears, choose More Advanced Options from the search assistant box. Another way is by clicking on All Files and Folders.
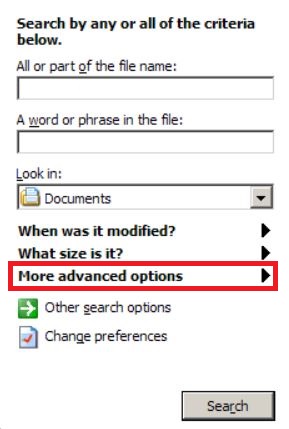
3: After that type the name of the file you are looking for and click on the Search button. This might take some time after which results will appear. If you have found the malicious file, you may copy or open its location by right-clicking on it.
Now you should be able to discover any file on Windows as long as it is on your hard drive and is not concealed via special software.
Trojan:Win32/Ravartar!rfn FAQ
What Does Trojan:Win32/Ravartar!rfn Trojan Do?
The Trojan:Win32/Ravartar!rfn Trojan is a malicious computer program designed to disrupt, damage, or gain unauthorized access to a computer system. It can be used to steal sensitive data, gain control over a system, or launch other malicious activities.
Can Trojans Steal Passwords?
Yes, Trojans, like Trojan:Win32/Ravartar!rfn, can steal passwords. These malicious programs are designed to gain access to a user's computer, spy on victims and steal sensitive information such as banking details and passwords.
Can Trojan:Win32/Ravartar!rfn Trojan Hide Itself?
Yes, it can. A Trojan can use various techniques to mask itself, including rootkits, encryption, and obfuscation, to hide from security scanners and evade detection.
Can a Trojan be Removed by Factory Reset?
Yes, a Trojan can be removed by factory resetting your device. This is because it will restore the device to its original state, eliminating any malicious software that may have been installed. Bear in mind that there are more sophisticated Trojans that leave backdoors and reinfect even after a factory reset.
Can Trojan:Win32/Ravartar!rfn Trojan Infect WiFi?
Yes, it is possible for a Trojan to infect WiFi networks. When a user connects to the infected network, the Trojan can spread to other connected devices and can access sensitive information on the network.
Can Trojans Be Deleted?
Yes, Trojans can be deleted. This is typically done by running a powerful anti-virus or anti-malware program that is designed to detect and remove malicious files. In some cases, manual deletion of the Trojan may also be necessary.
Can Trojans Steal Files?
Yes, Trojans can steal files if they are installed on a computer. This is done by allowing the malware author or user to gain access to the computer and then steal the files stored on it.
Which Anti-Malware Can Remove Trojans?
Anti-malware programs such as SpyHunter are capable of scanning for and removing Trojans from your computer. It is important to keep your anti-malware up to date and regularly scan your system for any malicious software.
Can Trojans Infect USB?
Yes, Trojans can infect USB devices. USB Trojans typically spread through malicious files downloaded from the internet or shared via email, allowing the hacker to gain access to a user's confidential data.
About the Trojan:Win32/Ravartar!rfn Research
The content we publish on SensorsTechForum.com, this Trojan:Win32/Ravartar!rfn how-to removal guide included, is the outcome of extensive research, hard work and our team’s devotion to help you remove the specific trojan problem.
How did we conduct the research on Trojan:Win32/Ravartar!rfn?
Please note that our research is based on an independent investigation. We are in contact with independent security researchers, thanks to which we receive daily updates on the latest malware definitions, including the various types of trojans (backdoor, downloader, infostealer, ransom, etc.)
Furthermore, the research behind the Trojan:Win32/Ravartar!rfn threat is backed with VirusTotal.
To better understand the threat posed by trojans, please refer to the following articles which provide knowledgeable details.