Trojan:JS/FakeCaptcha is one of the more sophisticated social engineering threats currently active, because it requires no exploit, no software vulnerability, and no drive-by download to succeed – it simply tricks the user into doing the work themselves. If you have seen a Microsoft Defender alert for this detection, or if you recall interacting with a CAPTCHA-style page that asked you to press keyboard shortcuts and paste something, it is critical to treat your system as potentially compromised and follow the full removal process below. What appeared to be a routine bot-check may have been the entry point for a serious infection.
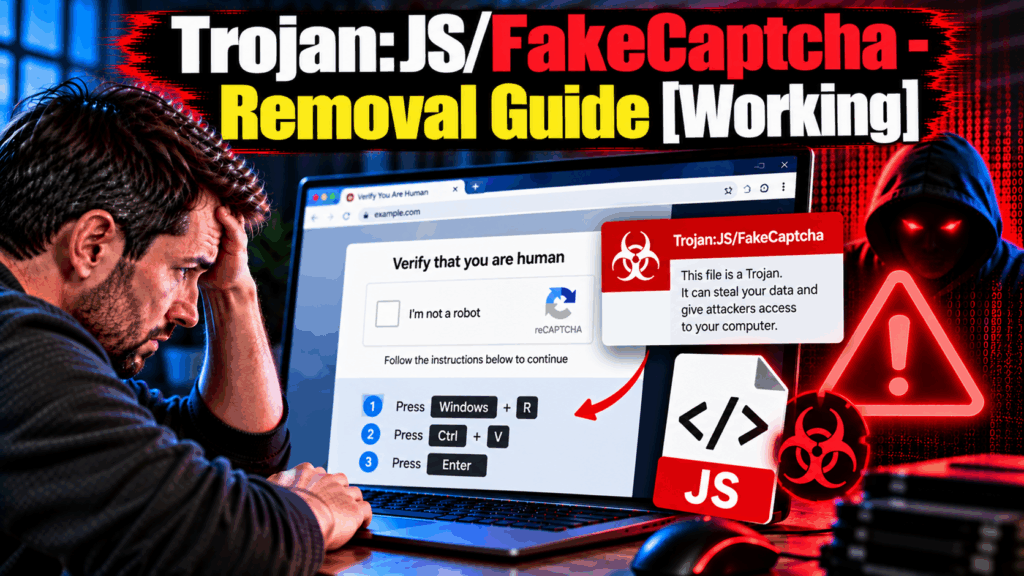
Trojan:JS/FakeCaptcha is a detection issued by Microsoft Defender Antivirus for malicious JavaScript that implements what security researchers call a “ClickFix” or fake CAPTCHA social engineering attack. As documented in Microsoft Security Intelligence, this technique presents the user with a page that looks like a standard CAPTCHA verification form, but instead of asking them to identify images, it instructs them to open the Windows Run dialog (Win + R), paste a command that has been silently loaded into the clipboard by the page’s JavaScript, and press Enter. The command is typically a PowerShell or mshta instruction that downloads and executes malware – and the entire process is completed by the user themselves, bypassing automated defenses.
| Name | Trojan:JS/FakeCaptcha |
| Threat Type | JavaScript Trojan / Social Engineering / ClickFix Attack (Microsoft Defender Detection) |
| Symptoms | Microsoft Defender alert for Trojan:JS/FakeCaptcha; encountering a fake CAPTCHA page that instructs pressing Windows+R and pasting a command; PowerShell or cmd window briefly appearing and closing unexpectedly; unexpected files appearing in temp directories following a fake CAPTCHA interaction; secondary malware installed after executing clipboard content from a fake verification page |
| Removal Time | Around 15 Minutes |
| Removal Tool | See If Your System Has Been Affected by Malware
* Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. SpyHunter’s EULA, Privacy Policy, and more details about Free Remover. |
How Did I Get Trojan:JS/FakeCaptcha?
The FakeCaptcha attack reaches users through several delivery channels, all dependent on the user reaching a page containing the malicious JavaScript:
- Compromised legitimate websites – websites with security vulnerabilities that have had the fake CAPTCHA JavaScript injected into their pages by attackers, meaning users visiting perfectly ordinary sites may suddenly see the fake verification prompt.
- Malicious advertising networks – ad content that redirects browser traffic to pages hosting the FakeCaptcha script when visitors arrive from specific sources or meet certain profiling criteria.
- SEO poisoning – fake pages optimized to rank in search results for common queries, leading users to FakeCaptcha-hosting pages when clicking on what appear to be legitimate search results.
- Phishing emails linking to pages that present the fake CAPTCHA verification as a prerequisite to viewing the linked content – an invoice, a document, a shared file, or a media item.
- Social media and forum links shared in communities with topics that attract users willing to click external links – gaming forums, software piracy communities, and adult content platforms have all been documented distribution vectors.
What Does Trojan:JS/FakeCaptcha Do?
The attack sequence and its consequences follow a consistent pattern:
- Displays a convincing fake verification page – the JavaScript generates a page visually similar to legitimate CAPTCHA interfaces used by major platforms, claiming a human verification step is required to proceed. The design may imitate specific well-known CAPTCHA providers to increase credibility.
- Silently loads a malicious command into the clipboard – while the user reads the fake instructions, the JavaScript uses clipboard APIs to replace any current clipboard content with a PowerShell, mshta, or cmd command that will download and execute malware when run.
- Instructs the user to paste and run the clipboard content – the fake instructions typically say “Press Windows+R, paste the verification code below, and press Enter” or “Open Run, type the code to complete verification.” The user is deceived into opening cmd or PowerShell and running the attacker’s command themselves.
- Executes a downloader payload – the pasted command contacts a remote server and downloads additional malware onto the system, which may include infostealers targeting browser credentials and crypto wallets, ransomware, remote access trojans, or coin miners.
- The secondary malware operates conventionally once on the system – establishing persistence, collecting data, or encrypting files depending on the specific payload chosen by the campaign operators at the time of execution.
How to Remove Trojan:JS/FakeCaptcha?
If you ran a command from a fake CAPTCHA page, treat this as an active compromise:
- Disconnect from the internet immediately to prevent active malware from communicating with command-and-control servers or exfiltrating data.
- Boot into Safe Mode with Networking – restart, hold Shift and click Restart, navigate to Troubleshoot – Advanced Options – Startup Settings, press 5. This prevents most downloaded payloads from loading at startup.
- Run a comprehensive full-system scan with SpyHunter in Safe Mode – the FakeCaptcha JavaScript itself is typically transient (a page script), but the payloads it downloaded and executed are real installed malware that require thorough detection and removal.
- Check %Temp% and %AppData% for recently created executable files, PowerShell scripts, or batch files – these locations are common staging areas for payloads downloaded through FakeCaptcha attacks.
- Review Task Scheduler and registry startup keys for entries created by downloaded payloads: Task Scheduler via Win + R – taskschd.msc, and registry via Win + R – regedit at HKEY_CURRENT_USERSoftwareMicrosoftWindowsCurrentVersionRun.
- Check for installed programs added around the time of the interaction, sorted by date in Settings – Apps.
- Run a second scan after restarting normally to confirm full removal of all downloaded components.
- Change all browser-stored passwords and account credentials from a clean device – if an infostealer was among the downloaded payloads, all credentials stored in the browser should be considered compromised.

Ventsislav Krastev
Ventsislav is a cybersecurity expert at SensorsTechForum since 2015. He has been researching, covering, helping victims with the latest malware infections plus testing and reviewing software and the newest tech developments. Having graduated Marketing as well, Ventsislav also has passion for learning new shifts and innovations in cybersecurity that become game changers. After studying Value Chain Management, Network Administration and Computer Administration of System Applications, he found his true calling within the cybersecrurity industry and is a strong believer in the education of every user towards online safety and security.
Follow Me:
Preparation before removing Trojan:JS/FakeCaptcha.
Before starting the actual removal process, we recommend that you do the following preparation steps.
- Make sure you have these instructions always open and in front of your eyes.
- Do a backup of all of your files, even if they could be damaged. You should back up your data with a cloud backup solution and insure your files against any type of loss, even from the most severe threats.
- Be patient as this could take a while.
- Scan for Malware
- Fix Registries
- Remove Virus Files
Step 1: Scan for Trojan:JS/FakeCaptcha with SpyHunter Anti-Malware Tool
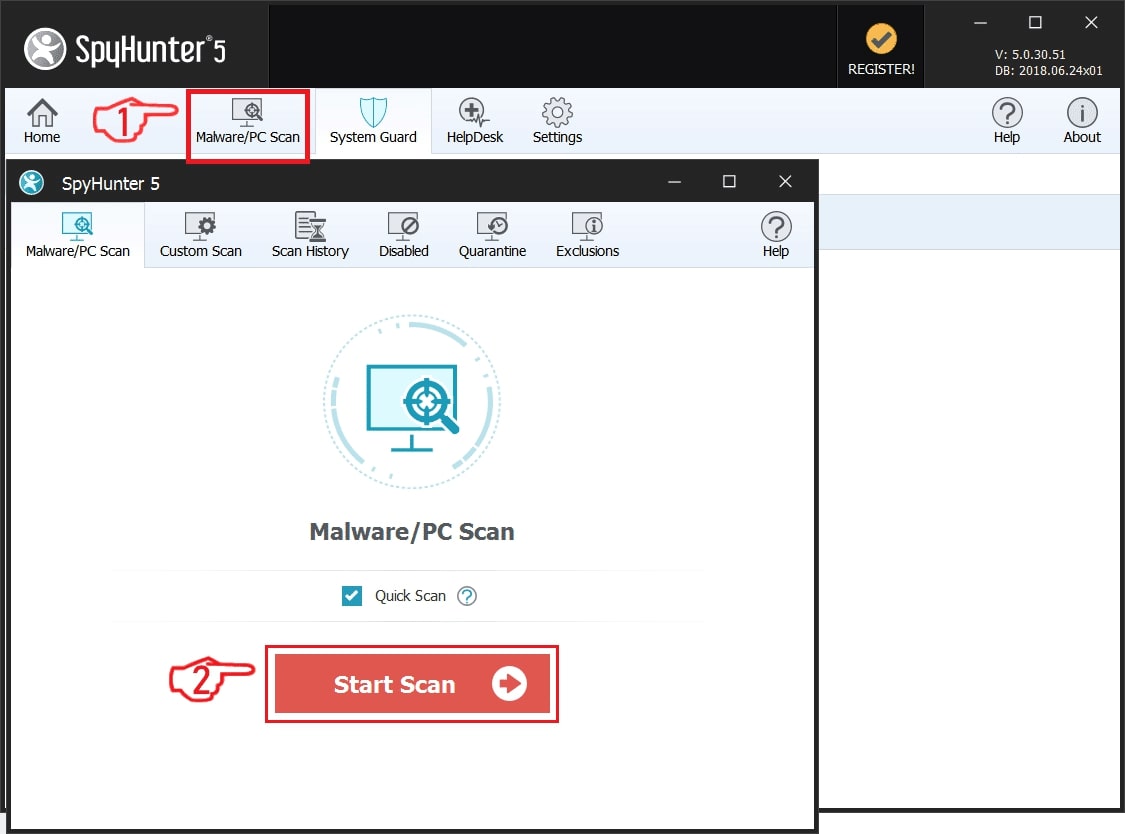
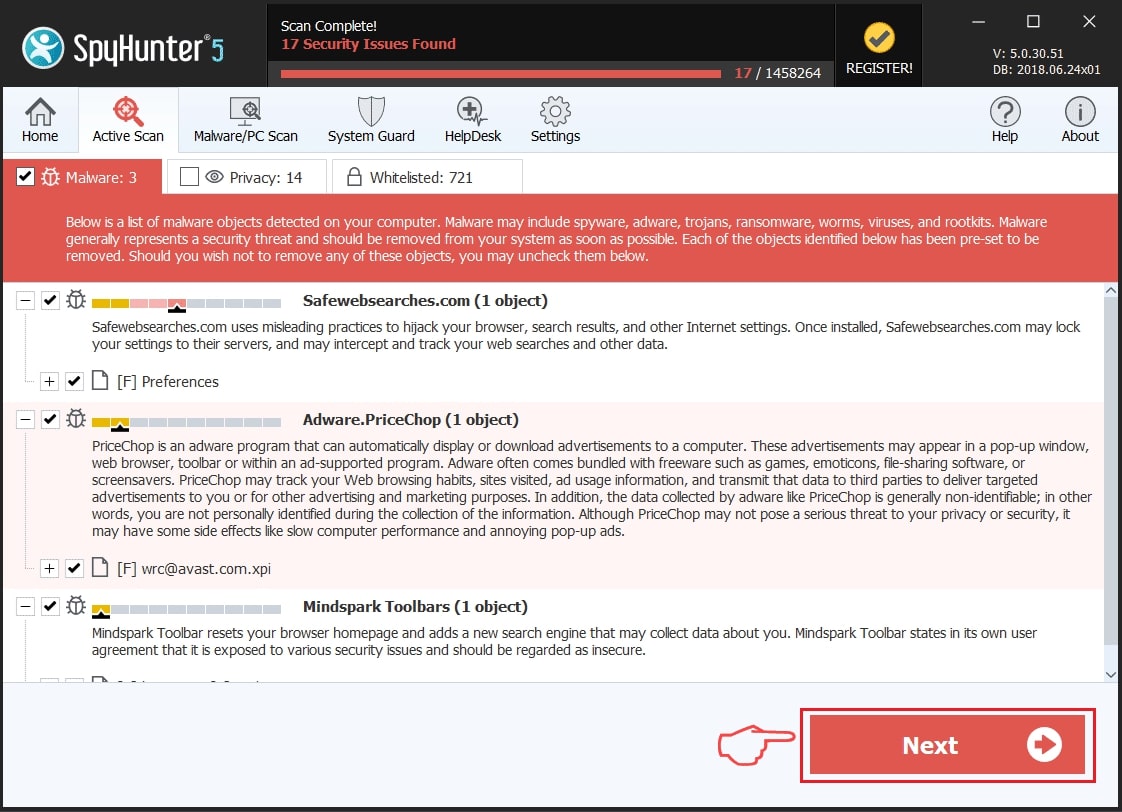
Step 2: Clean any registries, created by Trojan:JS/FakeCaptcha on your computer.
The usually targeted registries of Windows machines are the following:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
You can access them by opening the Windows registry editor and deleting any values, created by Trojan:JS/FakeCaptcha there. This can happen by following the steps underneath:
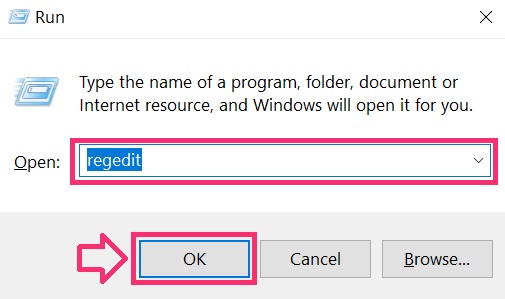
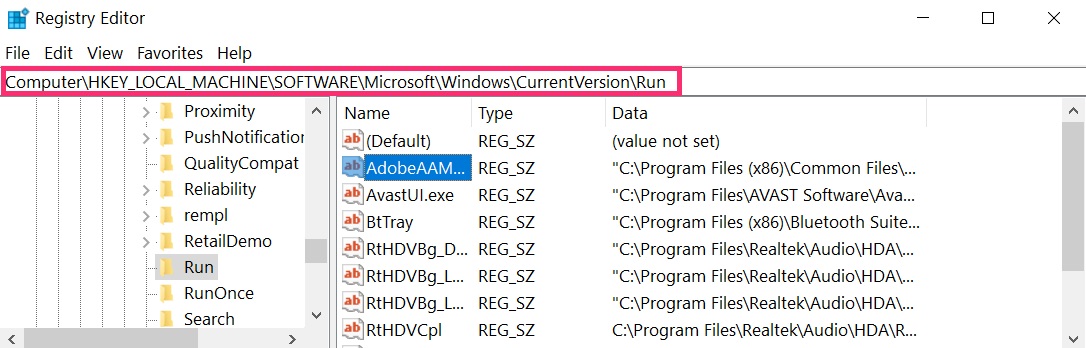
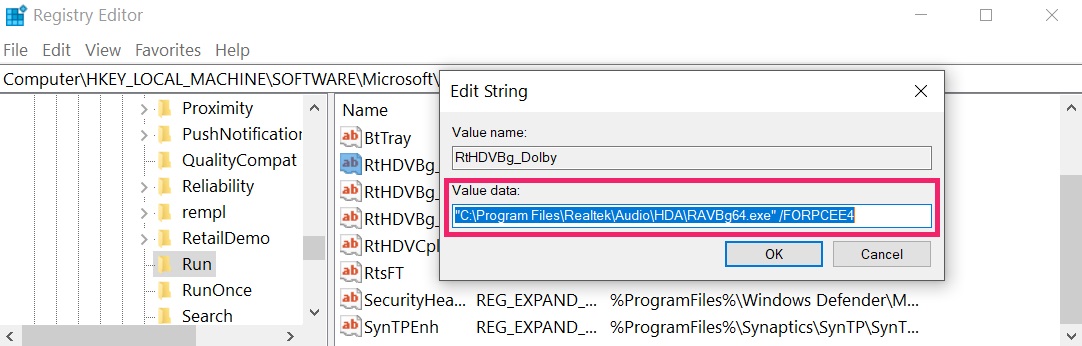 Tip: To find a virus-created value, you can right-click on it and click "Modify" to see which file it is set to run. If this is the virus file location, remove the value.
Step 3: Find virus files created by Trojan:JS/FakeCaptcha on your PC.
1.For Windows 8, 8.1 and 10.
For Newer Windows Operating Systems
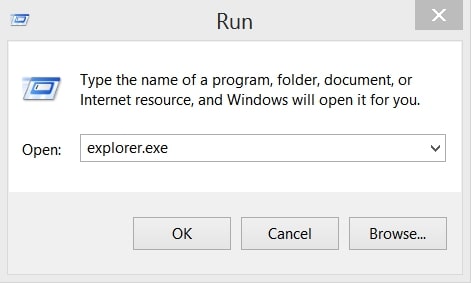
1: On your keyboard press + R and write explorer.exe in the Run text box and then click on the Ok button.
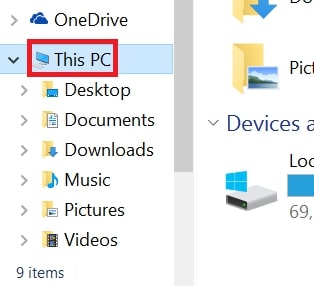
2: Click on your PC from the quick access bar. This is usually an icon with a monitor and its name is either “My Computer”, “My PC” or “This PC” or whatever you have named it.
3: Navigate to the search box in the top-right of your PC's screen and type “fileextension:” and after which type the file extension. If you are looking for malicious executables, an example may be "fileextension:exe". After doing that, leave a space and type the file name you believe the malware has created. Here is how it may appear if your file has been found:
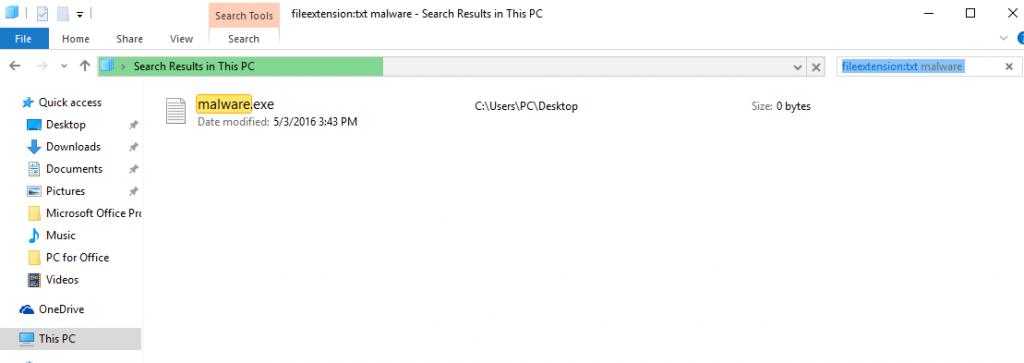
N.B. We recommend to wait for the green loading bar in the navigation box to fill up in case the PC is looking for the file and hasn't found it yet.
2.For Windows XP, Vista, and 7.
For Older Windows Operating Systems
In older Windows OS's the conventional approach should be the effective one:
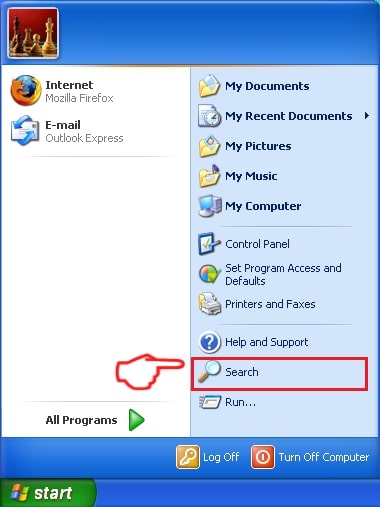
1: Click on the Start Menu icon (usually on your bottom-left) and then choose the Search preference.
2: After the search window appears, choose More Advanced Options from the search assistant box. Another way is by clicking on All Files and Folders.
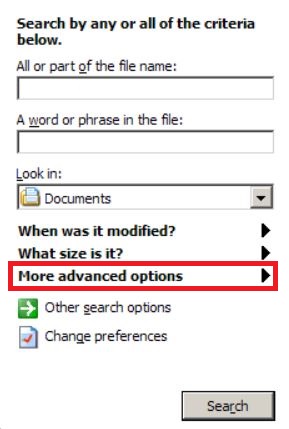
3: After that type the name of the file you are looking for and click on the Search button. This might take some time after which results will appear. If you have found the malicious file, you may copy or open its location by right-clicking on it.
Now you should be able to discover any file on Windows as long as it is on your hard drive and is not concealed via special software.
Trojan:JS/FakeCaptcha FAQ
What Does Trojan:JS/FakeCaptcha Trojan Do?
The Trojan:JS/FakeCaptcha Trojan is a malicious computer program designed to disrupt, damage, or gain unauthorized access to a computer system. It can be used to steal sensitive data, gain control over a system, or launch other malicious activities.
Can Trojans Steal Passwords?
Yes, Trojans, like Trojan:JS/FakeCaptcha, can steal passwords. These malicious programs are designed to gain access to a user's computer, spy on victims and steal sensitive information such as banking details and passwords.
Can Trojan:JS/FakeCaptcha Trojan Hide Itself?
Yes, it can. A Trojan can use various techniques to mask itself, including rootkits, encryption, and obfuscation, to hide from security scanners and evade detection.
Can a Trojan be Removed by Factory Reset?
Yes, a Trojan can be removed by factory resetting your device. This is because it will restore the device to its original state, eliminating any malicious software that may have been installed. Bear in mind that there are more sophisticated Trojans that leave backdoors and reinfect even after a factory reset.
Can Trojan:JS/FakeCaptcha Trojan Infect WiFi?
Yes, it is possible for a Trojan to infect WiFi networks. When a user connects to the infected network, the Trojan can spread to other connected devices and can access sensitive information on the network.
Can Trojans Be Deleted?
Yes, Trojans can be deleted. This is typically done by running a powerful anti-virus or anti-malware program that is designed to detect and remove malicious files. In some cases, manual deletion of the Trojan may also be necessary.
Can Trojans Steal Files?
Yes, Trojans can steal files if they are installed on a computer. This is done by allowing the malware author or user to gain access to the computer and then steal the files stored on it.
Which Anti-Malware Can Remove Trojans?
Anti-malware programs such as SpyHunter are capable of scanning for and removing Trojans from your computer. It is important to keep your anti-malware up to date and regularly scan your system for any malicious software.
Can Trojans Infect USB?
Yes, Trojans can infect USB devices. USB Trojans typically spread through malicious files downloaded from the internet or shared via email, allowing the hacker to gain access to a user's confidential data.
About the Trojan:JS/FakeCaptcha Research
The content we publish on SensorsTechForum.com, this Trojan:JS/FakeCaptcha how-to removal guide included, is the outcome of extensive research, hard work and our team’s devotion to help you remove the specific trojan problem.
How did we conduct the research on Trojan:JS/FakeCaptcha?
Please note that our research is based on an independent investigation. We are in contact with independent security researchers, thanks to which we receive daily updates on the latest malware definitions, including the various types of trojans (backdoor, downloader, infostealer, ransom, etc.)
Furthermore, the research behind the Trojan:JS/FakeCaptcha threat is backed with VirusTotal.
To better understand the threat posed by trojans, please refer to the following articles which provide knowledgeable details.