Virus:VBS/Ramnit is a serious and well-documented infection that requires more thorough remediation than most malware detections because Ramnit is a file-infecting virus – it does not just install itself on the system, it modifies existing files on the machine to embed copies of itself, making cleanup significantly more complex than removing a single executable. If Defender has flagged Virus:VBS/Ramnit, assume the infection extends beyond the initially detected file and follow the full removal procedure below. A partial removal that leaves infected files on the system is not a resolved infection.
Virus:VBS/Ramnit is the Visual Basic Script component of the Ramnit malware family, one of the most thoroughly documented file-infecting worms and banking trojans tracked by Microsoft Security Intelligence and security researchers globally. Ramnit, first identified in 2010 and active in continuously updated forms since, operates across multiple components: a file infector that modifies .exe, .dll, .htm, and .html files on the infected system to embed Ramnit code; a worm component that spreads through removable drives and network shares; and a banking trojan module that intercepts browser sessions with financial institutions to steal account credentials and session cookies. The VBS component specifically handles script-based propagation and payload execution.
| Name | Virus:VBS/Ramnit |
| Threat Type | File Infector Virus / Worm / Banking Trojan Component (Microsoft Defender Detection) |
| Symptoms | Microsoft Defender alert for Virus:VBS/Ramnit; multiple files on the system infected by the Ramnit virus; browser credential theft targeting banking and financial sites; Ramnit spreading to removable drives connected to the infected machine; HTML, executable, or script files modified by the virus without user action; system enrolled in Ramnit botnet operations |
| Removal Time | Around 15 Minutes |
| Removal Tool | See If Your System Has Been Affected by Malware
* Free Remover allows you, subject to a 48-hour waiting period, one remediation and removal for results found. SpyHunter’s EULA, Privacy Policy, and more details about Free Remover. |
How Did I Get Virus:VBS/Ramnit?
Ramnit spreads through multiple vectors, which contributes to its sustained prevalence:
- Infected removable drives – Ramnit’s worm component copies itself to USB drives, external hard drives, and memory cards connected to the infected machine, automatically executing when those drives are connected to another system with AutoRun enabled.
- File-sharing and torrent downloads – executable files downloaded from peer-to-peer networks or file-hosting platforms may already be infected by Ramnit if they originated from a Ramnit-infected machine.
- Compromised or malicious websites – drive-by download campaigns have historically distributed Ramnit through exploit kits targeting browser and plugin vulnerabilities.
- Malicious email attachments – script-based email attachment campaigns have been used to distribute Ramnit components, particularly the VBS propagation scripts.
- Network share propagation – in environments where multiple machines share network drives, Ramnit can spread from an infected machine to connected network shares, infecting files accessible to other users on the network.
What Does Virus:VBS/Ramnit Do?
The Ramnit family operates as a multi-function threat combining file infection, worm propagation, and financial data theft:
- Infects executable and HTML files on the system – Ramnit modifies .exe, .dll, .htm, and .html files by appending or embedding its code within them, meaning each infected file becomes a new carrier that can spread the infection when opened on another machine.
- Spreads to removable drives – every USB drive or external storage device connected to the infected machine receives a copy of Ramnit, making it a persistent infection vector that can carry the virus to entirely separate systems.
- Steals banking credentials and financial data – the Ramnit banking trojan module injects code into browser processes, intercepting HTTPS sessions with banking and financial sites to capture login credentials, one-time passwords, and session tokens before they are encrypted.
- Hijacks browser sessions through form grabbing and man-in-the-browser techniques that allow the operator to steal submitted data from any web form, including login credentials for email, social media, and other non-banking accounts.
- Enrolls the infected machine in the Ramnit botnet, making it available for distributed operations including spam distribution, credential theft relay, and further malware delivery at operator direction.
- Establishes persistent presence through registry modifications and service installation that survive reboots, with the file infection capability meaning new copies of the virus are continually created from infected files even if the original dropper is removed.
How to Remove Virus:VBS/Ramnit?
Ramnit’s file infection capability makes removal more involved than standard malware – infected files must either be cleaned or replaced:
- Disconnect all removable drives and external storage immediately to prevent the worm component from spreading further through connected devices.
- Disconnect from the network to interrupt Ramnit’s botnet communication and prevent spread across network shares.
- Boot into Safe Mode with Networking – restart, hold Shift and click Restart, navigate to Troubleshoot – Advanced Options – Startup Settings, press 5. Safe Mode prevents Ramnit from loading through its service and registry entries during cleanup.
- Run a full system scan with SpyHunter in Safe Mode. Because Ramnit infects multiple file types across the system, a thorough multi-engine scan is essential to identify all infected files rather than just the initially detected VBS component.
- Allow SpyHunter and Defender to clean or quarantine all detected infected files – do not skip detections. Files that cannot be cleaned should be quarantined and replaced from clean sources where possible.
- Scan removable drives that were connected to the machine before disconnecting them, treating any drive that was attached during the infection period as potentially carrying Ramnit copies.
- Restart normally and run a full second scan to confirm no infected files remain. Ramnit is persistent; a single scan pass is often insufficient for confirmation.
- Change all passwords for financial accounts, email, and social media from a clean device – Ramnit’s banking trojan component means all credentials entered in the browser during the infection period should be treated as compromised. Contact your bank if you accessed financial accounts on the infected machine.

Ventsislav Krastev
Ventsislav is a cybersecurity expert at SensorsTechForum since 2015. He has been researching, covering, helping victims with the latest malware infections plus testing and reviewing software and the newest tech developments. Having graduated Marketing as well, Ventsislav also has passion for learning new shifts and innovations in cybersecurity that become game changers. After studying Value Chain Management, Network Administration and Computer Administration of System Applications, he found his true calling within the cybersecrurity industry and is a strong believer in the education of every user towards online safety and security.
Follow Me:
Preparation before removing Virus:VBS/Ramnit.
Before starting the actual removal process, we recommend that you do the following preparation steps.
- Make sure you have these instructions always open and in front of your eyes.
- Do a backup of all of your files, even if they could be damaged. You should back up your data with a cloud backup solution and insure your files against any type of loss, even from the most severe threats.
- Be patient as this could take a while.
- Scan for Malware
- Fix Registries
- Remove Virus Files
Step 1: Scan for Virus:VBS/Ramnit with SpyHunter Anti-Malware Tool
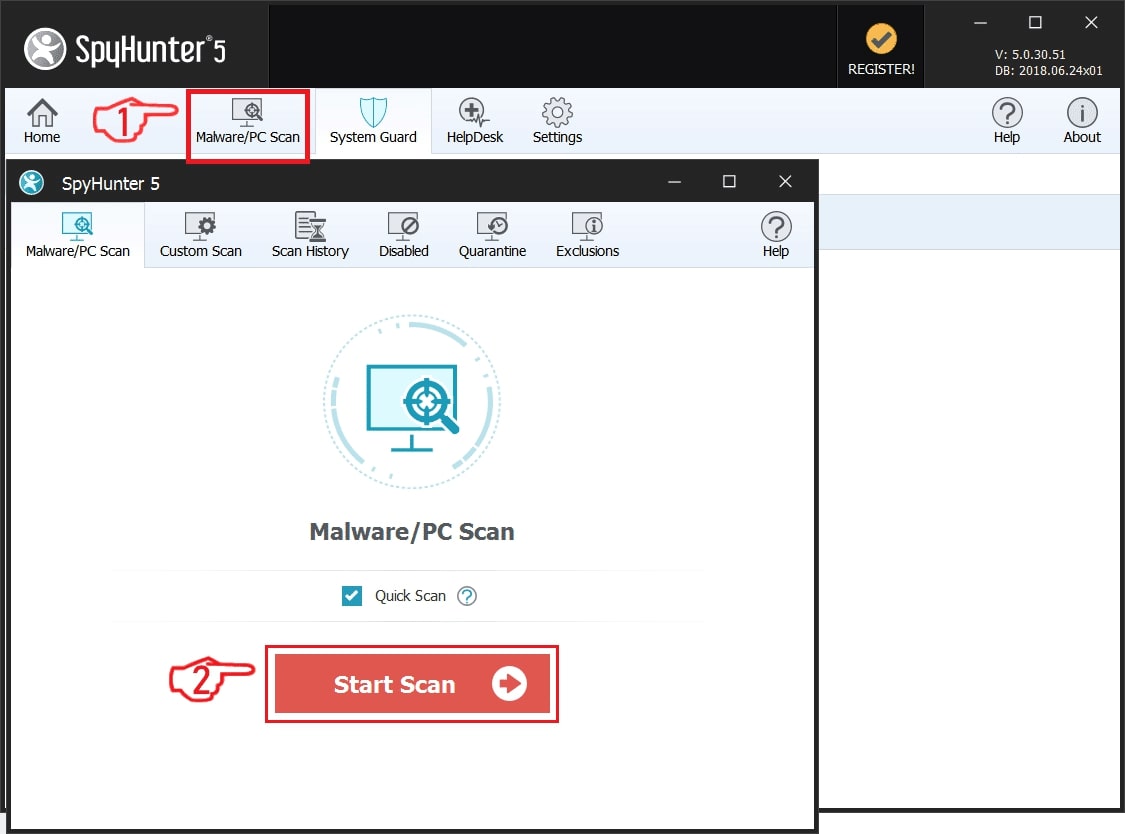
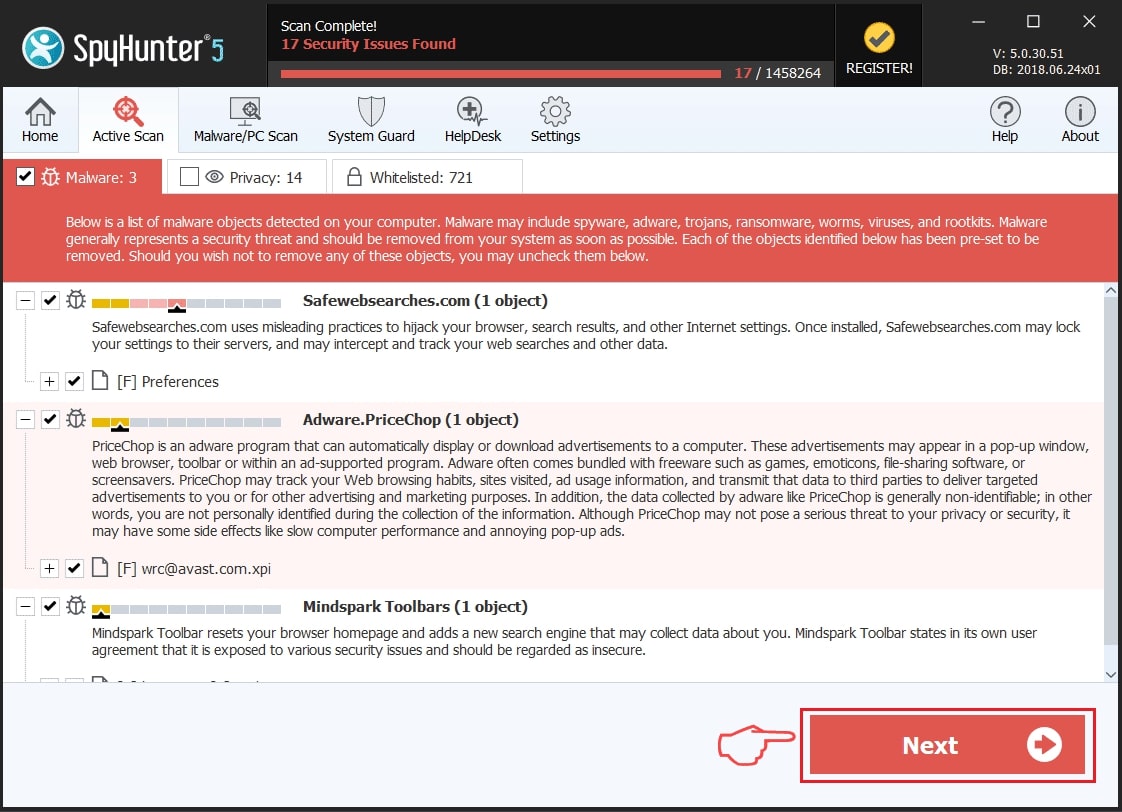
Step 2: Clean any registries, created by Virus:VBS/Ramnit on your computer.
The usually targeted registries of Windows machines are the following:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
You can access them by opening the Windows registry editor and deleting any values, created by Virus:VBS/Ramnit there. This can happen by following the steps underneath:
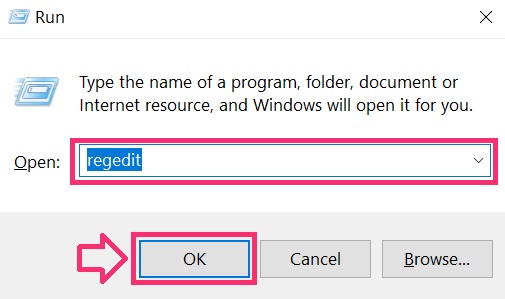
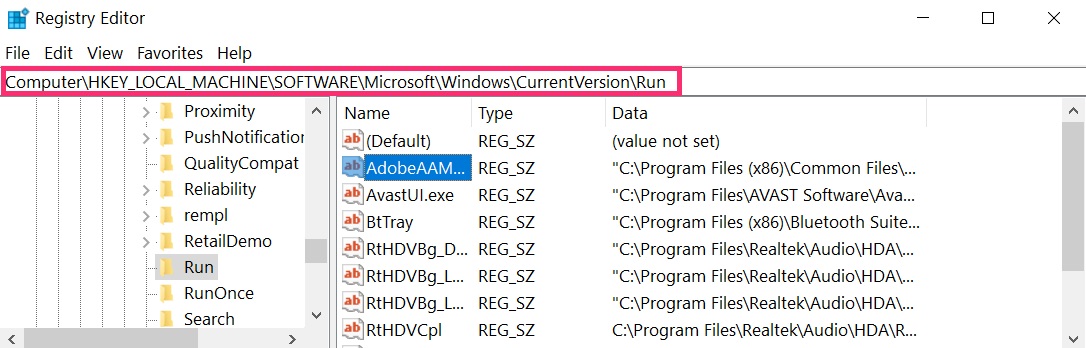
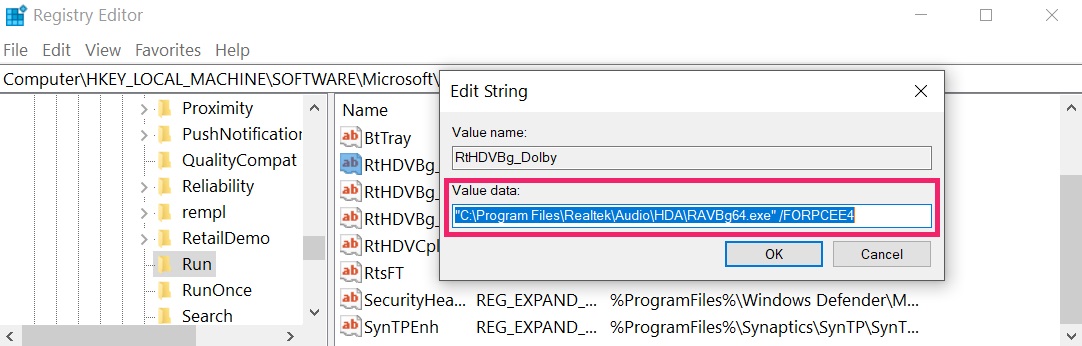 Tip: To find a virus-created value, you can right-click on it and click "Modify" to see which file it is set to run. If this is the virus file location, remove the value.
Step 3: Find virus files created by Virus:VBS/Ramnit on your PC.
1.For Windows 8, 8.1 and 10.
For Newer Windows Operating Systems
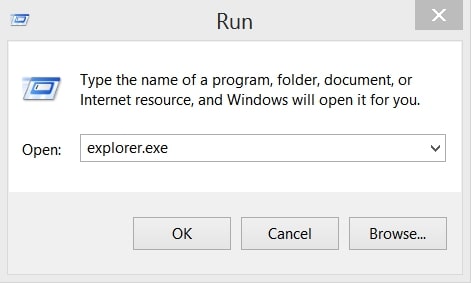
1: On your keyboard press + R and write explorer.exe in the Run text box and then click on the Ok button.
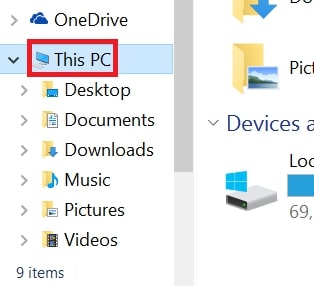
2: Click on your PC from the quick access bar. This is usually an icon with a monitor and its name is either “My Computer”, “My PC” or “This PC” or whatever you have named it.
3: Navigate to the search box in the top-right of your PC's screen and type “fileextension:” and after which type the file extension. If you are looking for malicious executables, an example may be "fileextension:exe". After doing that, leave a space and type the file name you believe the malware has created. Here is how it may appear if your file has been found:
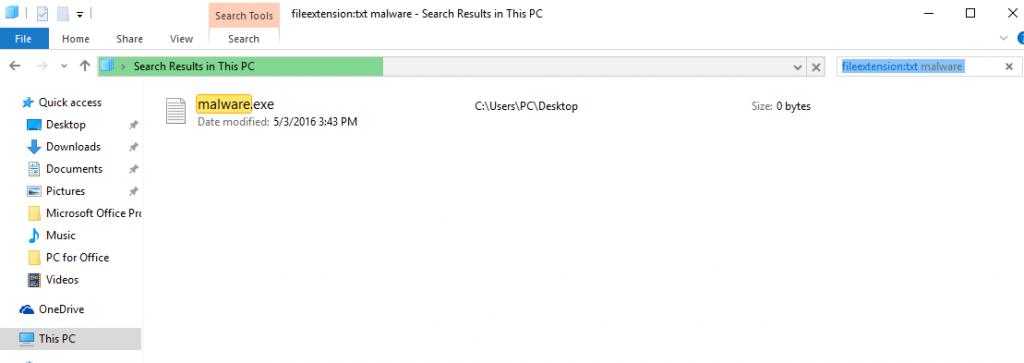
N.B. We recommend to wait for the green loading bar in the navigation box to fill up in case the PC is looking for the file and hasn't found it yet.
2.For Windows XP, Vista, and 7.
For Older Windows Operating Systems
In older Windows OS's the conventional approach should be the effective one:
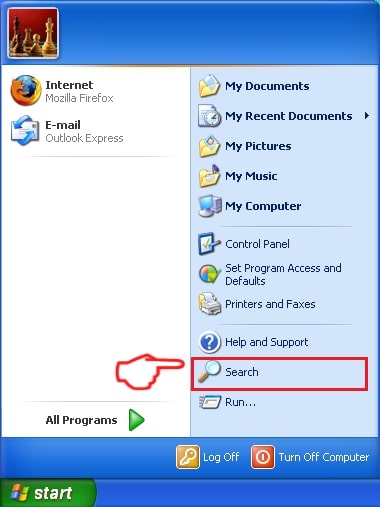
1: Click on the Start Menu icon (usually on your bottom-left) and then choose the Search preference.
2: After the search window appears, choose More Advanced Options from the search assistant box. Another way is by clicking on All Files and Folders.
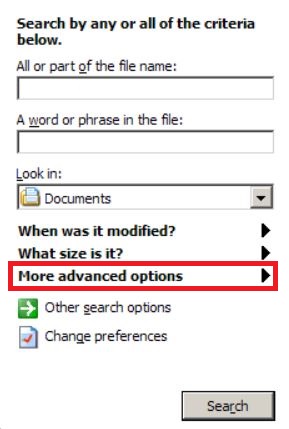
3: After that type the name of the file you are looking for and click on the Search button. This might take some time after which results will appear. If you have found the malicious file, you may copy or open its location by right-clicking on it.
Now you should be able to discover any file on Windows as long as it is on your hard drive and is not concealed via special software.
Virus:VBS/Ramnit FAQ
What Does Virus:VBS/Ramnit Trojan Do?
The Virus:VBS/Ramnit Trojan is a malicious computer program designed to disrupt, damage, or gain unauthorized access to a computer system. It can be used to steal sensitive data, gain control over a system, or launch other malicious activities.
Can Trojans Steal Passwords?
Yes, Trojans, like Virus:VBS/Ramnit, can steal passwords. These malicious programs are designed to gain access to a user's computer, spy on victims and steal sensitive information such as banking details and passwords.
Can Virus:VBS/Ramnit Trojan Hide Itself?
Yes, it can. A Trojan can use various techniques to mask itself, including rootkits, encryption, and obfuscation, to hide from security scanners and evade detection.
Can a Trojan be Removed by Factory Reset?
Yes, a Trojan can be removed by factory resetting your device. This is because it will restore the device to its original state, eliminating any malicious software that may have been installed. Bear in mind that there are more sophisticated Trojans that leave backdoors and reinfect even after a factory reset.
Can Virus:VBS/Ramnit Trojan Infect WiFi?
Yes, it is possible for a Trojan to infect WiFi networks. When a user connects to the infected network, the Trojan can spread to other connected devices and can access sensitive information on the network.
Can Trojans Be Deleted?
Yes, Trojans can be deleted. This is typically done by running a powerful anti-virus or anti-malware program that is designed to detect and remove malicious files. In some cases, manual deletion of the Trojan may also be necessary.
Can Trojans Steal Files?
Yes, Trojans can steal files if they are installed on a computer. This is done by allowing the malware author or user to gain access to the computer and then steal the files stored on it.
Which Anti-Malware Can Remove Trojans?
Anti-malware programs such as SpyHunter are capable of scanning for and removing Trojans from your computer. It is important to keep your anti-malware up to date and regularly scan your system for any malicious software.
Can Trojans Infect USB?
Yes, Trojans can infect USB devices. USB Trojans typically spread through malicious files downloaded from the internet or shared via email, allowing the hacker to gain access to a user's confidential data.
About the Virus:VBS/Ramnit Research
The content we publish on SensorsTechForum.com, this Virus:VBS/Ramnit how-to removal guide included, is the outcome of extensive research, hard work and our team’s devotion to help you remove the specific trojan problem.
How did we conduct the research on Virus:VBS/Ramnit?
Please note that our research is based on an independent investigation. We are in contact with independent security researchers, thanks to which we receive daily updates on the latest malware definitions, including the various types of trojans (backdoor, downloader, infostealer, ransom, etc.)
Furthermore, the research behind the Virus:VBS/Ramnit threat is backed with VirusTotal.
To better understand the threat posed by trojans, please refer to the following articles which provide knowledgeable details.