

What is PAY HERE Ransomware?
Your files have been encrypted and renamed with an unfamiliar extension, and a ransom note with “PAY HERE” instructions appeared on your desktop or in every affected folder demanding cryptocurrency payment for a decryption key. Read this guide carefully before doing anything, including paying – paying the ransom does not guarantee file recovery and sends money directly to criminals.
PAY HERE is a ransomware infection that encrypts personal files on the infected device using a strong cryptographic algorithm – documents, images, videos, databases, and other user-created files are targeted and rendered inaccessible. A distinctive file extension is appended to every encrypted file, and a ransom note is dropped on the desktop and in each affected folder with instructions directing the victim to contact the attackers and pay a ransom in cryptocurrency to receive a decryption key. The “PAY HERE” label in the ransom note is a social engineering element designed to reduce hesitation and push the victim toward payment before investigating alternatives. As documented across all ransomware families in this payment-demand category, paying the ransom does not guarantee receiving a working decryption key – a significant proportion of victims who pay receive a broken tool, receive nothing, or are targeted a second time because they have demonstrated willingness to pay. The ransomware itself must be removed immediately to prevent further encryption of any remaining files. Whether encrypted files can be recovered depends on the specific encryption implementation and whether a decryptor has been published by security researchers or law enforcement.
PAY HERE Short Overview
| Type | Ransomware that encrypts personal files (documents, images, videos, databases) and appends a custom extension, rendering them inaccessible. Drops a “PAY HERE” ransom note demanding cryptocurrency payment for a decryption key. Attempts to delete Windows Shadow Volume Copies to prevent free recovery. Paying the ransom does not guarantee file recovery. File recovery options: check nomoreransom.org for a free decryptor matching the exact variant, restore from a clean offline backup, or use data recovery tools if Shadow Copies were not fully deleted. |
| Symptoms | Personal files (documents, images, videos) suddenly inaccessible with an unfamiliar extension appended to every filename. A ransom note file (typically a .txt or .html file) appearing on the desktop and in every affected folder with PAY HERE payment instructions. Desktop wallpaper changed to a ransom demand message. Windows Shadow Volume Copies deleted (no System Restore points available). Security software disabled or preventing normal operation. Unusual disk activity from all drives during the encryption process. |
| Removal Time | Approximately 15 minutes for a full-system scan |
| Removal Tool | See If Your System Has Been Affected by malware
Download
Malware Removal Tool
|
How Did I Get PAY HERE Ransomware?
Ransomware in this category arrives through these documented delivery routes:
- Phishing emails with malicious attachments or links – The most documented route for ransomware delivery: a convincingly formatted email presents an invoice, delivery notification, or document that, when opened, executes a macro or script that downloads and runs the ransomware installer on the device.
- Cracked software and pirated application installers – Ransomware is consistently embedded in cracked application packages, key generators, and pirated software downloaded from unofficial sources. The ransomware executes automatically during setup, often before the user sees any unexpected behavior.
- Software bundling with unofficial free downloads – A free utility from a third-party site installs the ransomware dropper through software bundling alongside the expected program.
- Remote Desktop Protocol exploitation – Attackers scan for Windows systems with RDP exposed and weak or reused credentials, then log in remotely and manually execute the ransomware on the network – a common enterprise and home-server attack route.
What Does PAY HERE Ransomware Do?
- Encrypts personal files and appends a ransom extension – PAY HERE ransomware scans all local drives and, in networked environments, mapped network drives for personal files including documents, images, videos, and archives. Each targeted file is encrypted and a new extension is appended, making the file inaccessible without the decryption key.
- Drops a ransom note in every affected folder and on the desktop – A text or HTML ransom note is placed in every folder containing encrypted files and on the desktop, providing contact information, payment instructions in Bitcoin or another cryptocurrency, and a deadline or threat of permanent data loss to create urgency.
- Attempts to delete Shadow Volume Copies to prevent free recovery – Most ransomware in this demand category runs a command to delete Windows Shadow Volume Copies – the automatic backups Windows creates through the Volume Shadow Copy Service – to prevent victims from restoring files for free. This command is documented across confirmed ransomware families as a standard post-encryption step.
- May disable or interfere with security software – Some variants attempt to kill antivirus processes or add themselves to Windows Defender exclusions before or during encryption to prevent the encryption process from being interrupted.
Removal & File Recovery Guide
Do not pay the ransom. Paying does not guarantee file recovery and funds further criminal operations. Here is the correct sequence of actions:
Step 1 – Isolate the infected device immediately. Disconnect from all networks (unplug ethernet, turn off Wi-Fi) to prevent the ransomware from spreading to network shares, mapped drives, or other connected devices. Do not reconnect until the device is fully cleaned.
Step 2 – Do not delete any encrypted files. Make a full backup of the encrypted files on an external drive or a second offline storage location before doing anything else. If a decryptor is published by security researchers at a later date, you will need the encrypted files to use it.
Step 3 – Identify the ransomware. Upload the ransom note and a sample encrypted file (under 1 MB, with no sensitive data) to ID Ransomware at id-ransomware.malwarehunterteam.com to identify the exact variant. This step determines whether a free decryptor already exists.
Step 4 – Check for a free decryptor. Visit nomoreransom.org and search for the identified variant. Free decryptors are published by Europol, law enforcement partners, Emsisoft, Avast, and Bitdefender for many ransomware families. If one exists for your variant, download it from the official source only – not from third-party sites claiming to have decryptors, as these frequently distribute additional malware.
Step 5 – Remove the ransomware. Boot into Safe Mode (hold Shift and click Restart, then Troubleshoot, then Advanced Options, then Startup Settings, then Restart, then press 5 or F5 for Safe Mode with Networking). Run a full system scan with SpyHunter or another dedicated anti-malware tool to remove the ransomware executable and any persistence components. Do not attempt to restore files until the ransomware is fully removed, or the restored files will be re-encrypted.
Step 6 – Restore from backup if available. If a clean offline or cloud backup predating the infection exists, restore from it after confirming the ransomware has been fully removed. Check the backup’s last-modified date to ensure it predates the encryption event.
Follow the complete removal and file recovery guide below this article for the full step-by-step process.

Ventsislav Krastev
Ventsislav is a cybersecurity expert at SensorsTechForum since 2015. He has been researching, covering, helping victims with the latest malware infections plus testing and reviewing software and the newest tech developments. Having graduated Marketing as well, Ventsislav also has passion for learning new shifts and innovations in cybersecurity that become game changers. After studying Value Chain Management, Network Administration and Computer Administration of System Applications, he found his true calling within the cybersecrurity industry and is a strong believer in the education of every user towards online safety and security.
Follow Me:
- Step 1
- Step 2
- Step 3
- Step 4
- Step 5
Step 1: Scan for PAY HERE with SpyHunter Anti-Malware Tool
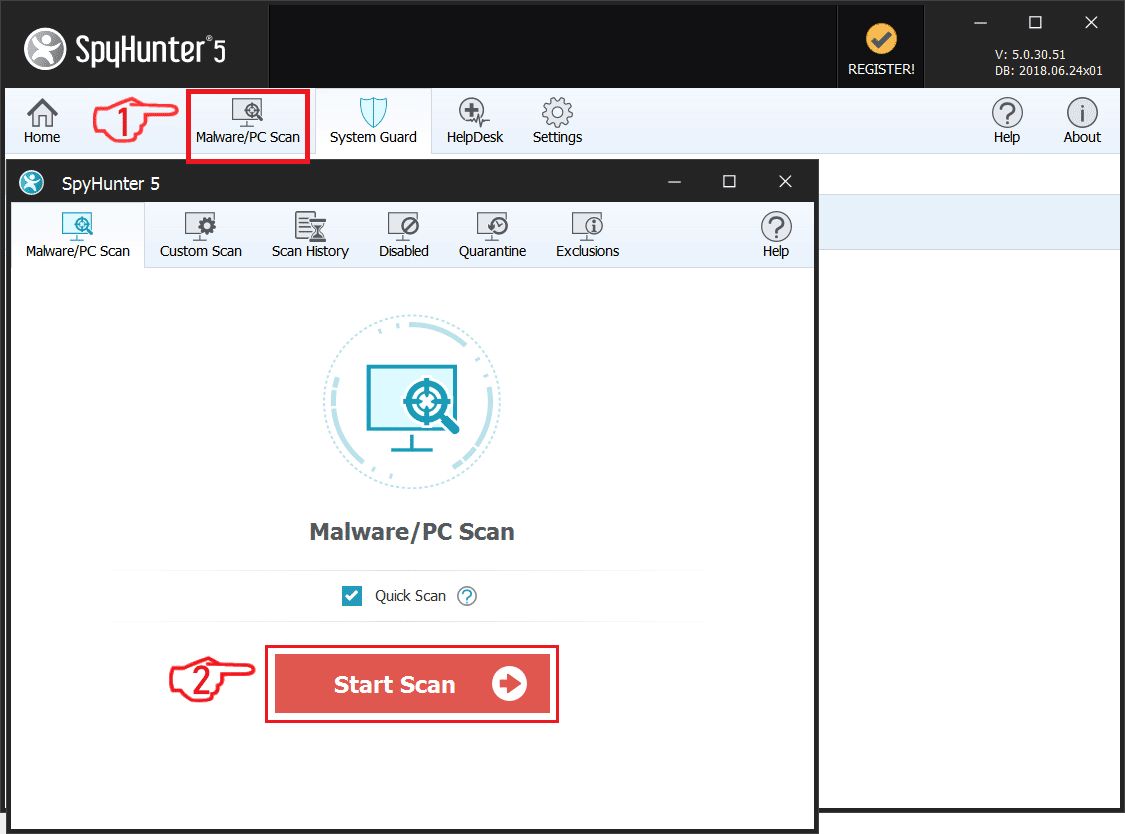
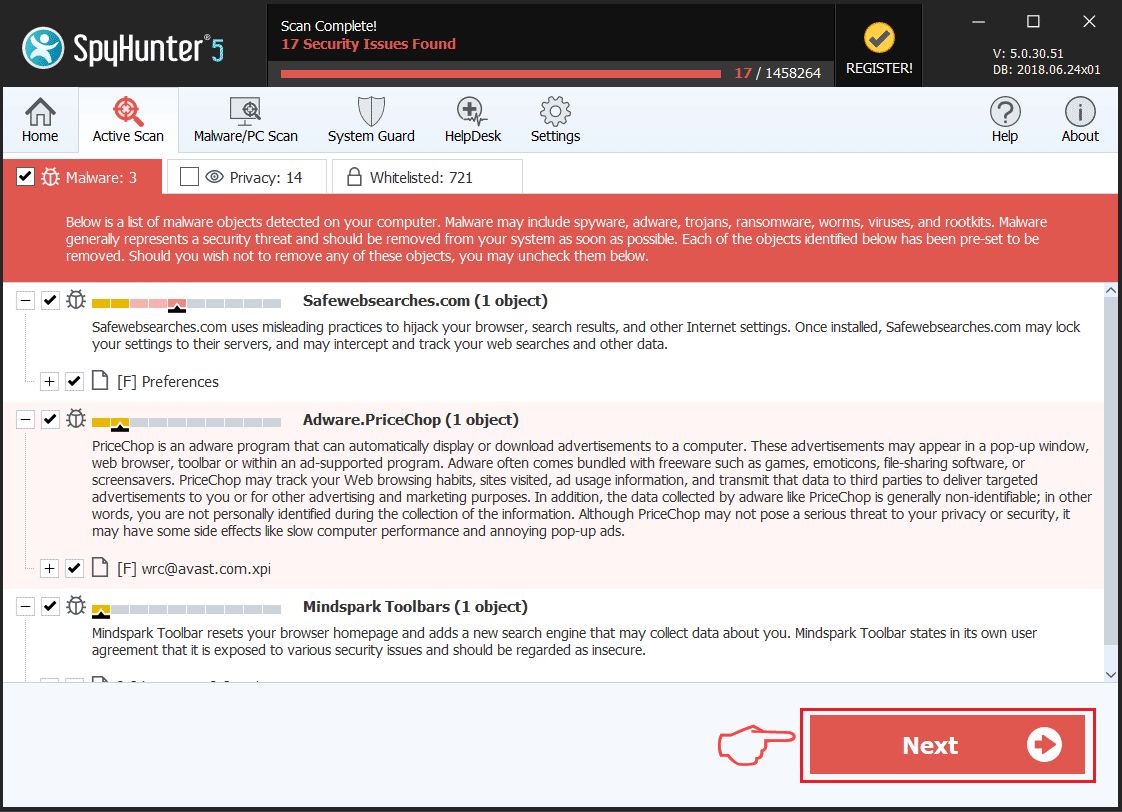
Ransomware Automatic Removal - Video Guide
Step 2: Uninstall PAY HERE and related malware from Windows
Here is a method in few easy steps that should be able to uninstall most programs. No matter if you are using Windows 10, 8, 7, Vista or XP, those steps will get the job done. Dragging the program or its folder to the recycle bin can be a very bad decision. If you do that, bits and pieces of the program are left behind, and that can lead to unstable work of your PC, errors with the file type associations and other unpleasant activities. The proper way to get a program off your computer is to Uninstall it. To do that:
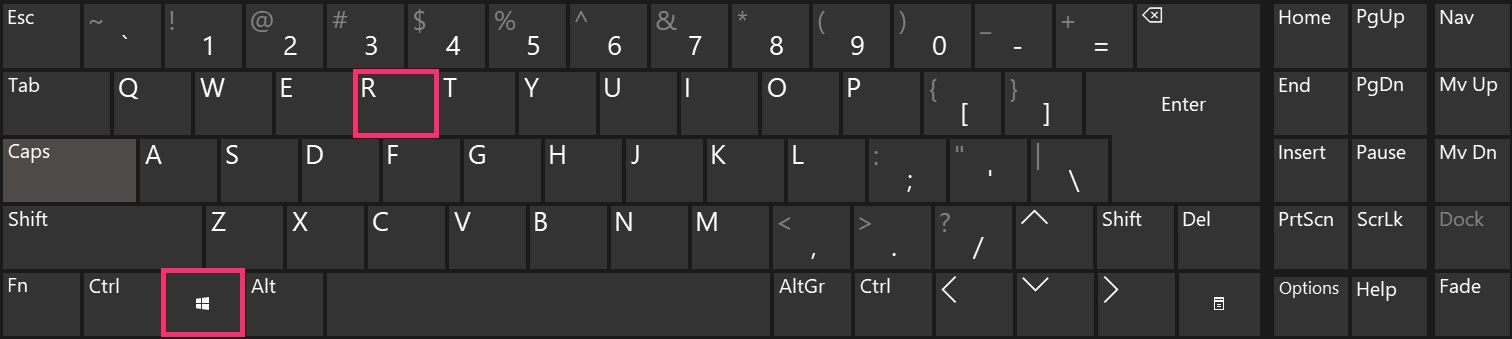
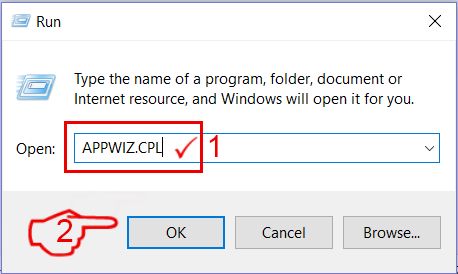
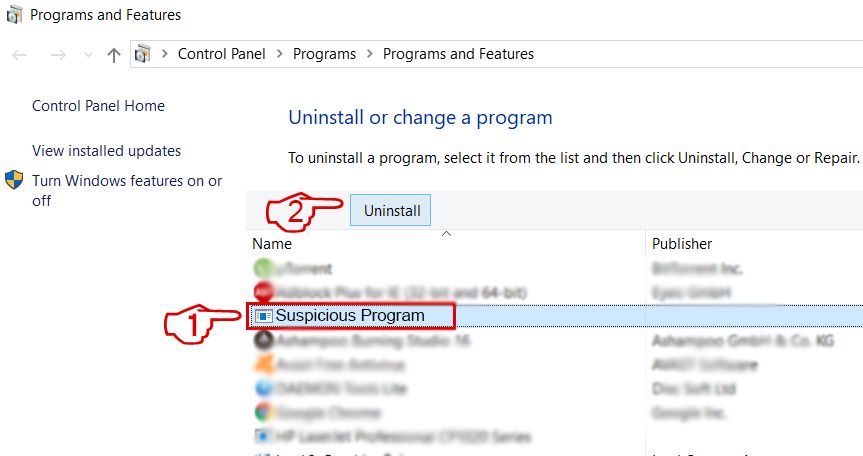 Follow the instructions above and you will successfully delete most unwanted and malicious programs.
Step 3: Clean any registries, created by PAY HERE on your computer.
The usually targeted registries of Windows machines are the following:
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
- HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\RunOnce
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\RunOnce
You can access them by opening the Windows registry editor and deleting any values, created by PAY HERE there. This can happen by following the steps underneath:


 Tip: To find a virus-created value, you can right-click on it and click "Modify" to see which file it is set to run. If this is the virus file location, remove the value.
Before starting "Step 4", please boot back into Normal mode, in case you are currently in Safe Mode.
This will enable you to install and use SpyHunter 5 successfully.
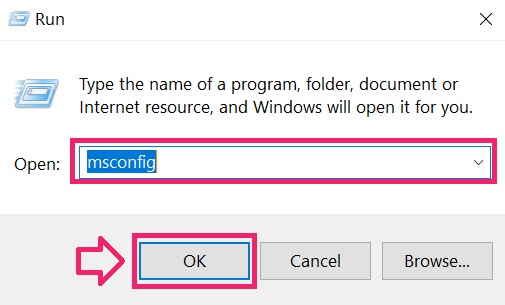
Step 4: Boot Your PC In Safe Mode to isolate and remove PAY HERE
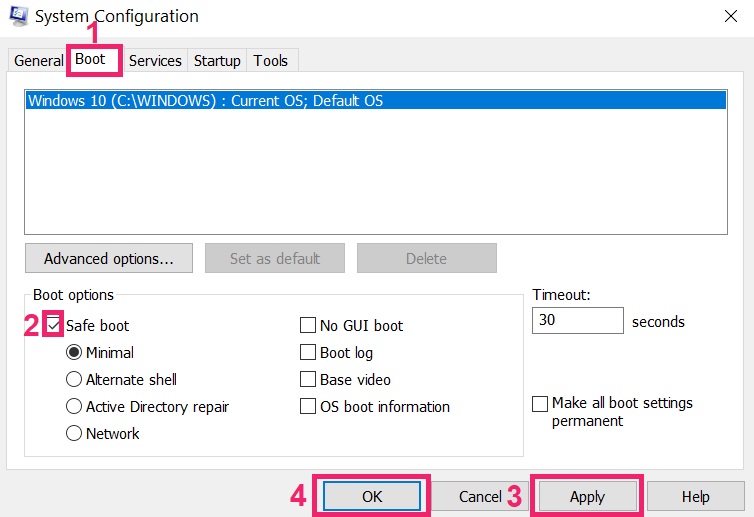
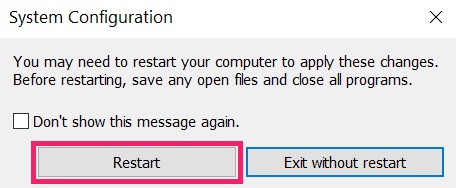
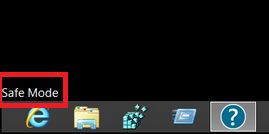
Step 5: Try to Restore Files Encrypted by PAY HERE.
Method 1: Use STOP Decrypter by Emsisoft.
Not all variants of this ransomware can be decrypted for free, but we have added the decryptor used by researchers that is often updated with the variants which become eventually decrypted. You can try and decrypt your files using the instructions below, but if they do not work, then unfortunately your variant of the ransomware virus is not decryptable.
Follow the instructions below to use the Emsisoft decrypter and decrypt your files for free. You can download the Emsisoft decryption tool linked here and then follow the steps provided below:
1 Right-click on the decrypter and click on Run as Administrator as shown below:
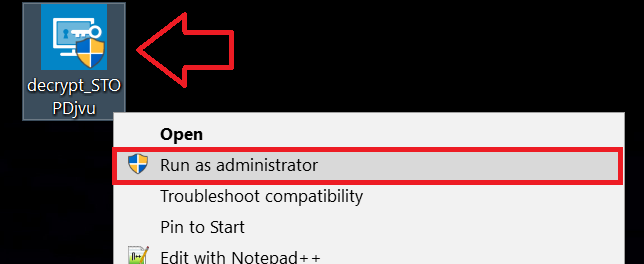
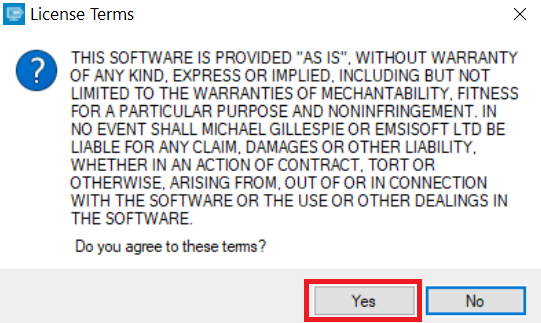
2. Agree with the license terms:
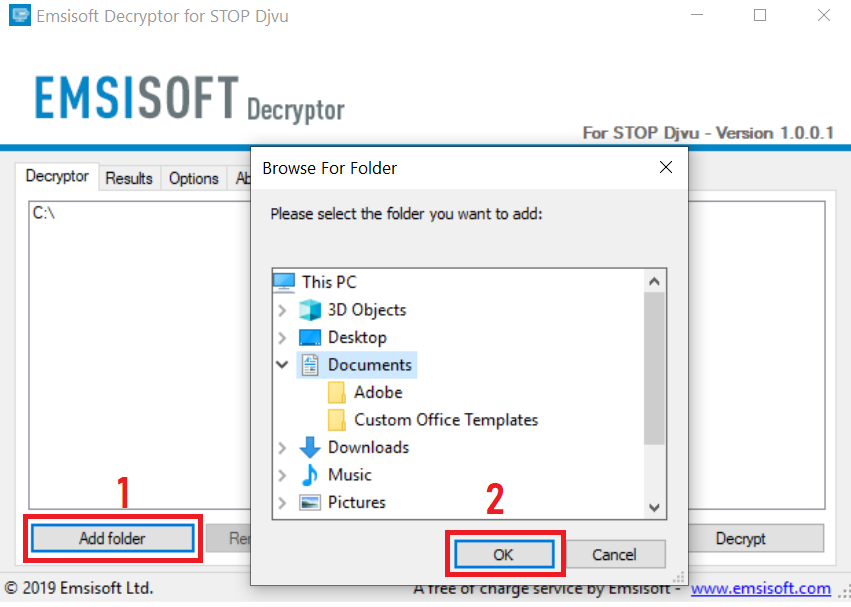
3. Click on "Add Folder" and then add the folders where you want files decrypted as shown underneath:
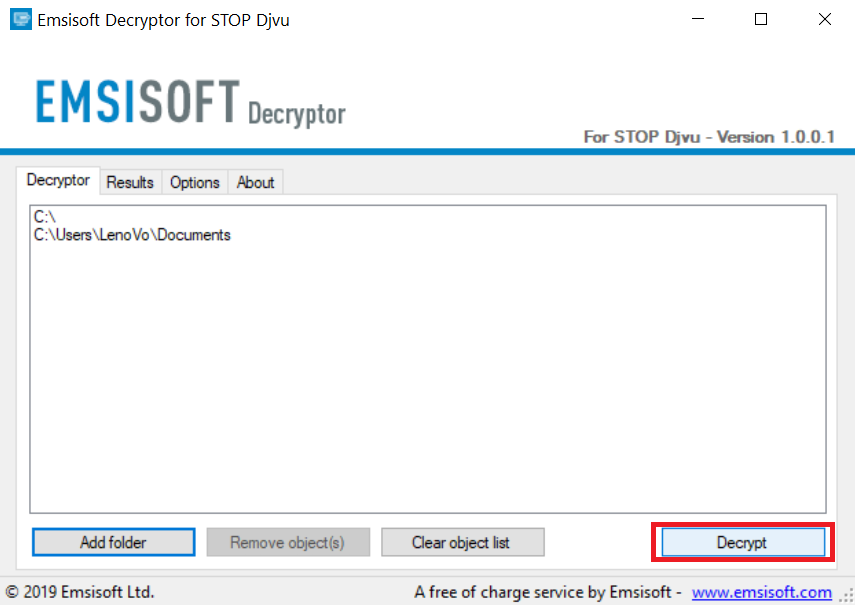
4. Click on "Decrypt" and wait for your files to be decoded.
Note: Credit for the decryptor goes to Emsisoft researchers who have made the breakthrough with this virus.
Method 2: Use data recovery software
Ransomware infections and PAY HERE aim to encrypt your files using an encryption algorithm which may be very difficult to decrypt. This is why we have suggested a data recovery method that may help you go around direct decryption and try to restore your files. Bear in mind that this method may not be 100% effective but may also help you a little or a lot in different situations.
Simply click on the link and on the website menus on the top, choose Data Recovery - Data Recovery Wizard for Windows or Mac (depending on your OS), and then download and run the tool.
PAY HERE-FAQ
What is PAY HERE Ransomware?
PAY HERE is a ransomware infection - the malicious software that enters your computer silently and blocks either access to the computer itself or encrypt your files.
Many ransomware viruses use sophisticated encryption algorithms to make your files inaccessible. The goal of ransomware infections is to demand that you pay a ransom payment to get access to your files back.
What Does PAY HERE Ransomware Do?
Ransomware in general is a malicious software that is designed to block access to your computer or files until a ransom is paid.
Ransomware viruses can also damage your system, corrupt data and delete files, resulting in the permanent loss of important files.
How Does PAY HERE Infect?
Via several ways.PAY HERE Ransomware infects computers by being sent via phishing emails, containing virus attachment. This attachment is usually masked as an important document, like an invoice, bank document or even a plane ticket and it looks very convincing to users.
Another way you may become a victim of PAY HERE is if you download a fake installer, crack or patch from a low reputation website or if you click on a virus link. Many users report getting a ransomware infection by downloading torrents.
How to Open .PAY HERE files?
You can't without a decryptor. At this point, the .PAY HERE files are encrypted. You can only open them once they are decrypted using a specific decryption key for the particular algorithm.
What to Do If a Decryptor Does Not Work?
Do not panic, and backup the files. If a decryptor did not decrypt your .PAY HERE files successfully, then do not despair, because this virus is still new.
Can I Restore ".PAY HERE" Files?
Yes, sometimes files can be restored. We have suggested several file recovery methods that could work if you want to restore .PAY HERE files.
These methods are in no way 100% guaranteed that you will be able to get your files back. But if you have a backup, your chances of success are much greater.
How To Get Rid of PAY HERE Virus?
The safest way and the most efficient one for the removal of this ransomware infection is the use a professional anti-malware program.
It will scan for and locate PAY HERE ransomware and then remove it without causing any additional harm to your important .PAY HERE files.
Can I Report Ransomware to Authorities?
In case your computer got infected with a ransomware infection, you can report it to the local Police departments. It can help authorities worldwide track and determine the perpetrators behind the virus that has infected your computer.
Below, we have prepared a list with government websites, where you can file a report in case you are a victim of a cybercrime:
Cyber-security authorities, responsible for handling ransomware attack reports in different regions all over the world:
Germany - Offizielles Portal der deutschen Polizei
United States - IC3 Internet Crime Complaint Centre
United Kingdom - Action Fraud Police
France - Ministère de l'Intérieur
Italy - Polizia Di Stato
Spain - Policía Nacional
Netherlands - Politie
Poland - Policja
Portugal - Polícia Judiciária
Greece - Cyber Crime Unit (Hellenic Police)
India - Mumbai Police - CyberCrime Investigation Cell
Australia - Australian High Tech Crime Center
Reports may be responded to in different timeframes, depending on your local authorities.
Can You Stop Ransomware from Encrypting Your Files?
Yes, you can prevent ransomware. The best way to do this is to ensure your computer system is updated with the latest security patches, use a reputable anti-malware program and firewall, backup your important files frequently, and avoid clicking on malicious links or downloading unknown files.
Can PAY HERE Ransomware Steal Your Data?
Yes, in most cases ransomware will steal your information. It is a form of malware that steals data from a user's computer, encrypts it, and then demands a ransom in order to decrypt it.
In many cases, the malware authors or attackers will threaten to delete the data or publish it online unless the ransom is paid.
Can Ransomware Infect WiFi?
Yes, ransomware can infect WiFi networks, as malicious actors can use it to gain control of the network, steal confidential data, and lock out users. If a ransomware attack is successful, it could lead to a loss of service and/or data, and in some cases, financial losses.
Should I Pay Ransomware?
No, you should not pay ransomware extortionists. Paying them only encourages criminals and does not guarantee that the files or data will be restored. The better approach is to have a secure backup of important data and be vigilant about security in the first place.
What Happens If I Don't Pay Ransom?
If you don't pay the ransom, the hackers may still have access to your computer, data, or files and may continue to threaten to expose or delete them, or even use them to commit cybercrimes. In some cases, they may even continue to demand additional ransom payments.
Can a Ransomware Attack Be Detected?
Yes, ransomware can be detected. Anti-malware software and other advanced security tools can detect ransomware and alert the user when it is present on a machine.
It is important to stay up-to-date on the latest security measures and to keep security software updated to ensure ransomware can be detected and prevented.
Do Ransomware Criminals Get Caught?
Yes, ransomware criminals do get caught. Law enforcement agencies, such as the FBI, Interpol and others have been successful in tracking down and prosecuting ransomware criminals in the US and other countries. As ransomware threats continue to increase, so does the enforcement activity.
About the PAY HERE Research
The content we publish on SensorsTechForum.com, this PAY HERE how-to removal guide included, is the outcome of extensive research, hard work and our team’s devotion to help you remove the specific malware and restore your encrypted files.
How did we conduct the research on this ransomware?
Our research is based on an independent investigation. We are in contact with independent security researchers, and as such, we receive daily updates on the latest malware and ransomware definitions.
Furthermore, the research behind the PAY HERE ransomware threat is backed with VirusTotal and the NoMoreRansom project.
To better understand the ransomware threat, please refer to the following articles which provide knowledgeable details.
As a site that has been dedicated to providing free removal instructions for ransomware and malware since 2014, SensorsTechForum’s recommendation is to only pay attention to trustworthy sources.
How to recognize trustworthy sources:
- Always check "About Us" web page.
- Profile of the content creator.
- Make sure that real people are behind the site and not fake names and profiles.
- Verify Facebook, LinkedIn and Twitter personal profiles.